Untitled
[JUDUL] What is Penetration Testing in Software Testing and Why It Matters Now
[META_DESCRIPTION] Understand what is penetration testing in software testing, its methods, benefits, comparison, and future trends in cybersecurity.
[TAGS] penetration testing, software testing, cybersecurity, ethical hacking, security testing
[CATEGORY] General
[/KONTEN]
The Complete Overview of Penetration Testing in Software Testing
Penetration testing, often referred to as ethical hacking, is a controlled and authorized simulated cyberattack conducted against an organization’s computer systems, networks, applications, or other digital assets. The primary objective is to identify, evaluate, and document security vulnerabilities that could be exploited by malicious actors. When integrated into the broader framework of software testing, penetration testing serves as a critical validation mechanism, ensuring that software products meet defined security standards before they are deployed in production environments.
Table of Contents
- The Complete Overview of Penetration Testing in Software Testing
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What is penetration testing in software testing?
- Q: How does penetration testing differ from vulnerability assessment?
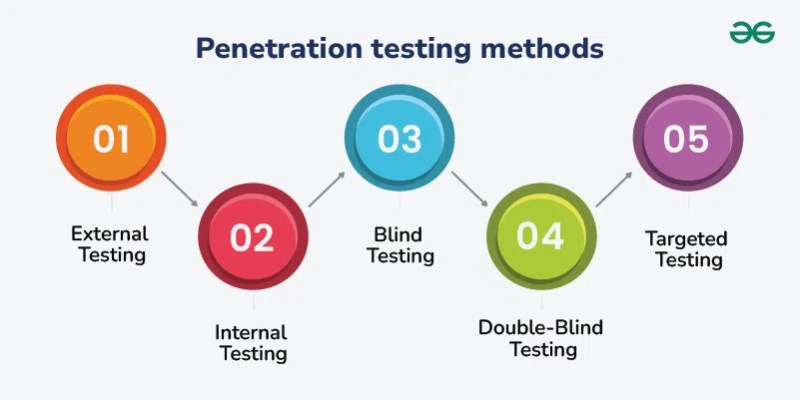
- Q: What are the different types of penetration testing?
- Q: How often should penetration testing be performed?
- Q: What qualifications should a penetration tester have?
- Q: What is the typical methodology followed in penetration testing?
- Q: How are penetration test results documented and reported?
The practice involves a structured methodology where security professionals, known as penetration testers or ethical hackers, systematically attempt to breach the target system using the same techniques and tools employed by real-world attackers. This process typically includes reconnaissance, scanning, enumeration, gaining access, maintaining access, and covering tracks. Each phase is meticulously documented, allowing organizations to understand not only the vulnerabilities present but also the potential impact of their exploitation. In the context of software testing, this approach provides a dynamic assessment that complements static and dynamic code analysis, offering a holistic view of an application’s security posture.
As cyber threats continue to evolve in sophistication and scale, traditional defensive measures alone are no longer sufficient to protect sensitive data and critical infrastructure. Organizations across industries are increasingly adopting proactive security strategies, integrating penetration testing as a core component of their software development lifecycle (SDLC). This shift reflects a growing recognition that security must be embedded from the earliest stages of development rather than being an afterthought. By understanding what penetration testing in software testing entails, stakeholders can make informed decisions about resource allocation, risk management, and compliance requirements, ultimately safeguarding their digital ecosystems against emerging threats.
Historical Background and Evolution
The origins of penetration testing can be traced back to the late 1960s and early 1970s, when the U.S. Department of Defense began conducting security evaluations of its computer systems. These early exercises were primarily focused on identifying vulnerabilities in mainframe operating systems and network architectures. One of the pioneering figures in this field was hacker Kevin Mitnick, who, after being apprehended for his unauthorized activities, transitioned into a legitimate career as a security consultant. His experiences highlighted the importance of simulating real-world attack scenarios to test the resilience of systems and networks.
Over the decades, penetration testing has evolved significantly, driven by technological advancements and the increasing complexity of digital environments. The emergence of the internet in the 1990s introduced new attack vectors, prompting the development of more sophisticated testing methodologies. The term "ethical hacking" gained prominence during this period, as security professionals sought to distinguish their authorized activities from those of malicious hackers. Today, penetration testing encompasses a wide range of domains, including web application security, mobile application testing, network penetration testing, and social engineering assessments. Regulatory frameworks such as the Payment Card Industry Data Security Standard (PCI DSS) and the General Data Protection Regulation (GDPR) have further institutionalized penetration testing as a mandatory practice for organizations handling sensitive information.
Core Mechanisms: How It Works
At its core, penetration testing follows a structured five-phase methodology that mirrors the tactics used by actual attackers. The first phase, reconnaissance, involves gathering preliminary information about the target system through passive or active means. This may include analyzing publicly available data, conducting domain name system (DNS) lookups, or performing WHOIS queries. The second phase, scanning and enumeration, utilizes specialized tools to identify live hosts, open ports, and running services. Techniques such as port scanning, vulnerability scanning, and banner grabbing help testers map the attack surface and pinpoint potential entry points.
The third phase, gaining access, involves exploiting identified vulnerabilities to penetrate the target system. Testers may employ techniques such as SQL injection, cross-site scripting (XSS), or buffer overflow attacks to gain unauthorized access. Once inside, the fourth phase, maintaining access, focuses on establishing persistence within the system to simulate long-term compromise. This often includes creating backdoor accounts, modifying system configurations, or deploying malware. The final phase, covering tracks, involves removing evidence of the intrusion to avoid detection, allowing testers to assess the effectiveness of monitoring and incident response capabilities.
Key Benefits and Crucial Impact
The integration of penetration testing into software testing processes offers numerous strategic advantages for organizations seeking to enhance their cybersecurity posture. One of the most significant benefits is the ability to proactively identify vulnerabilities before they can be exploited by malicious actors. Unlike reactive security measures that respond to incidents after they occur, penetration testing enables organizations to adopt a preventive approach, reducing the likelihood of costly data breaches and associated reputational damage. Additionally, penetration testing provides valuable insights into the effectiveness of existing security controls, helping organizations prioritize remediation efforts and allocate resources more efficiently.
Beyond vulnerability identification, penetration testing plays a crucial role in regulatory compliance and risk management. Many industry standards and government regulations mandate regular security assessments as part of an organization’s overall governance framework. For example, financial institutions subject to the Gramm-Leach-Bliley Act (GLBA) and healthcare organizations governed by the Health Insurance Portability and Accountability Act (HIPAA) must demonstrate due diligence in protecting sensitive data. Penetration testing not only fulfills these compliance requirements but also provides auditable evidence of an organization’s commitment to maintaining robust security practices. Furthermore, the findings from penetration tests can inform security awareness training programs, helping employees recognize and respond to potential threats more effectively.
"Penetration testing is not just about finding vulnerabilities; it's about understanding the mindset of attackers and building defenses that can withstand real-world threats."
Major Advantages
- Proactive Threat Detection: Identifies security weaknesses before they can be exploited, reducing the risk of data breaches and financial losses.
- Compliance Validation: Ensures adherence to industry regulations and standards, providing documented evidence of security maturity for audits.
- Enhanced Risk Assessment: Provides actionable intelligence on potential attack vectors and their business impact, enabling informed decision-making.
- Improved Incident Response: Tests and refines incident response procedures, ensuring teams are prepared to handle real security incidents effectively.
- Cost Efficiency: Detects vulnerabilities early in the development cycle, avoiding expensive post-deployment fixes and minimizing downtime.

Comparative Analysis
| Vulnerability Assessment | Penetration Testing |
|---|---|
| Automated scanning tools identify known vulnerabilities without exploiting them. | Actively exploits vulnerabilities to determine exploitability and potential impact. |
| Provides a broad overview of security posture with minimal manual intervention. | Requires skilled professionals to simulate real-world attacks and interpret results. |
| Suitable for continuous monitoring and routine checks. | Conducted periodically for in-depth security validation and compliance purposes. |
| Less resource-intensive but may produce false positives. | More resource-intensive but delivers precise, actionable findings with minimal false positives. |
Future Trends and Innovations
As cyber threats become increasingly sophisticated, the landscape of penetration testing is undergoing rapid transformation. One of the most notable trends is the integration of artificial intelligence (AI) and machine learning (ML) technologies to automate and enhance testing processes. AI-powered tools can analyze vast amounts of data to identify patterns and anomalies that may indicate security vulnerabilities, reducing the time and effort required for manual testing. Additionally, the rise of DevSecOps practices is driving the incorporation of automated security testing into continuous integration and continuous deployment (CI/CD) pipelines, enabling organizations to detect and remediate vulnerabilities at every stage of the software development lifecycle.
Another emerging trend is the adoption of bug bounty programs and crowdsourced security testing platforms. These initiatives leverage the collective expertise of a global community of security researchers to identify vulnerabilities that internal teams may overlook. As organizations face an ever-expanding attack surface due to cloud computing, Internet of Things (IoT) devices, and remote work environments, the demand for flexible and scalable security testing solutions continues to grow. The future of penetration testing lies in combining traditional methodologies with innovative technologies and collaborative approaches to stay ahead of evolving cyber threats.

Conclusion
In conclusion, penetration testing represents a vital component of modern software testing practices, offering organizations a proactive means of identifying and mitigating security vulnerabilities. As cyber threats continue to evolve in complexity and scale, the ability to simulate real-world attack scenarios and assess the effectiveness of existing security controls becomes increasingly critical. By integrating penetration testing into their development processes, organizations can not only comply with regulatory requirements but also build more resilient software systems that can withstand sophisticated attacks.
The future of penetration testing will likely be shaped by advancements in automation, artificial intelligence, and collaborative security models. However, regardless of technological developments, the fundamental principles of thorough planning, meticulous execution, and comprehensive reporting will remain essential. Organizations that invest in robust penetration testing programs today will be better positioned to navigate the challenges of an increasingly interconnected and threat-laden digital landscape.
Comprehensive FAQs
Q: What is penetration testing in software testing?
A: Penetration testing in software testing is a controlled security assessment where ethical hackers simulate real-world attacks on software applications to identify, evaluate, and document vulnerabilities before malicious actors can exploit them. It is a critical component of the software development lifecycle that helps ensure applications meet security standards.
Q: How does penetration testing differ from vulnerability assessment?
A: While vulnerability assessment uses automated tools to scan for known vulnerabilities without exploiting them, penetration testing goes further by actively attempting to exploit identified weaknesses to assess their real-world impact. This makes penetration testing more comprehensive and actionable in terms of risk evaluation.
Q: What are the different types of penetration testing?
A: Common types include network penetration testing, web application testing, mobile application testing, wireless network testing, social engineering assessments, and database penetration testing. Each type targets specific components or layers of an organization’s digital infrastructure.
Q: How often should penetration testing be performed?
A: Penetration testing should be conducted at least annually and after any major system changes, updates, or deployments. Regulatory requirements may also mandate more frequent testing. Regular assessments help ensure ongoing security as threats and technologies evolve.
Q: What qualifications should a penetration tester have?
A: Professional penetration testers typically hold certifications such as Certified Ethical Hacker (CEH), Offensive Security Certified Professional (OSCP), or GIAC Penetration Tester (GPEN). Strong technical knowledge, analytical skills, and familiarity with security tools and methodologies are also essential.
Q: What is the typical methodology followed in penetration testing?
A: Most penetration tests follow a five-phase approach: reconnaissance, scanning and enumeration, gaining access, maintaining access, and covering tracks. This methodology mirrors the tactics used by real attackers and ensures a thorough evaluation of the target system’s security posture.
Q: How are penetration test results documented and reported?
A: Results are compiled into a detailed report that includes identified vulnerabilities, their severity levels, proof-of-concept exploits, potential business impact, and recommended remediation steps. Reports also provide executive summaries for stakeholders and technical details for development teams.
[/KONTEN]
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.