What Is an MD5 Checksum? The Hidden Math Behind Digital Trust

When a file downloads at 100MB/s but the moment it finishes, you’re hit with a nagging doubt: Did it corrupt mid-transfer? That’s where what is an MD5 checksum becomes your silent guardian. It’s not just a string of hexadecimal characters—it’s a mathematical fingerprint, a 128-bit signature that tells you, with near-certainty, whether your data has stayed intact. Governments, corporations, and even peer-to-peer networks rely on it to verify software updates, validate backups, and detect tampering in real time. Yet for all its ubiquity, most users treat it like a black box: run the command, compare the hash, and move on. The truth is far more fascinating—it’s a product of 1990s cryptography, a balance between speed and security that now faces an identity crisis in an era of quantum computing.
The MD5 checksum isn’t just about files. It’s embedded in protocols you interact with daily: SSL certificates, Git version control, and even blockchain’s Merkle trees. When you see those 32-character strings (like `d41d8cd98f00b204e9800998ecf8427e`), they’re the result of a deterministic process—always the same input yields the same output. But here’s the catch: what is an MD5 checksum isn’t just a tool; it’s a cautionary tale. While it excels at detecting accidental corruption, its collision vulnerabilities (where two different files produce the same hash) have forced industries to migrate to stronger alternatives like SHA-256. The question isn’t if you’ll encounter MD5, but how you’ll wield it—knowing its strengths, its limits, and the ethical dilemmas of its continued use.
The Complete Overview of What Is an MD5 Checksum
At its core, what is an MD5 checksum refers to a hash value generated by the MD5 (Message-Digest Algorithm 5) cryptographic function. Developed by Ronald Rivest in 1991 as part of the RSA Data Security suite, MD5 was designed to be a fast, one-way function that could take any input—be it a text document, binary file, or even a block of encrypted data—and produce a fixed-size 128-bit fingerprint. This fingerprint, when converted to hexadecimal, becomes the familiar 32-character string (e.g., `5f4dcc3b5aa765d61d8327deb882cf99`). The genius of MD5 lies in its determinism: the same file will always yield the same hash, while even the tiniest alteration—flipping a single bit—will produce a drastically different output. This property makes it ideal for data integrity verification, ensuring that a downloaded ISO, a critical database backup, or a firmware update hasn’t been corrupted or tampered with during transit.Yet the term "what is an MD5 checksum" is often conflated with its broader purpose. Technically, MD5 is a hash function, while the checksum is the resulting value. The confusion arises because in practice, users "check" the hash to verify the checksum’s integrity. MD5’s simplicity is both its strength and its Achilles’ heel. It’s computationally efficient—capable of hashing gigabytes of data in seconds—making it perfect for large-scale applications like distributed file systems. However, its efficiency comes at a cost: by the early 2000s, cryptanalysts had demonstrated that MD5’s design was vulnerable to collision attacks, where two distinct inputs produce the same hash. This flaw doesn’t invalidate MD5 for all uses (it’s still fine for non-security-critical checks), but it has forced industries to adopt stronger successors like SHA-256 for applications requiring cryptographic security.
Historical Background and Evolution
MD5’s origins trace back to the 1980s, when cryptographic hash functions were emerging as a solution to the problem of digital verification. Rivest’s earlier work, MD4 (1990), laid the groundwork, but it was quickly broken by collisions. MD5 refined the algorithm by adding an extra round of processing and tweaking the bitwise operations, aiming to close those vulnerabilities. For a decade, it reigned supreme: adopted by the IETF for securing email (RFC 1321), embedded in protocols like SSL/TLS, and even used by the FBI’s cryptographic standards. Its ubiquity stemmed from a perfect storm of factors: it was free, fast, and—at the time—considered secure enough for most non-military applications. By 1996, MD5 was the de facto standard for checksumming, appearing in everything from Linux kernels to Adobe Photoshop’s file validation.The cracks began to show in 2004, when cryptographers like Xiaoyun Wang and Hongbo Yu published the first practical collision attacks on MD5. Their work demonstrated that with enough computational power, it was possible to generate two different files (like a malicious PDF and a benign one) that produced identical hashes. This wasn’t just theoretical: in 2008, researchers created a pair of images that fooled MD5 into believing they were identical. The damage was done. While MD5 remained useful for non-security applications (e.g., detecting accidental corruption), its use in digital signatures, SSL certificates, and code-signing was deprecated by organizations like NIST and the IETF. Today, what is an MD5 checksum is often framed as a relic—one that persists in legacy systems but is increasingly replaced by SHA-2 or SHA-3 for critical operations.
Core Mechanisms: How It Works
Understanding what is an MD5 checksum requires peeling back the layers of its algorithmic design. MD5 processes input data in 512-bit chunks, padding the final chunk if necessary to ensure the total length is a multiple of 512 bits. The algorithm then applies four rounds of bitwise operations—each round consisting of 16 steps—that mix the input data with a set of predefined constants and nonlinear functions. These operations include:The result is a 128-bit hash, which is then typically rendered as a 32-character hexadecimal string. The key insight is that MD5 is not reversible: given the hash, you cannot derive the original input. This one-way property is what makes it useful for checksumming. Even a single-bit change in the input will, on average, alter half of the bits in the hash, making accidental corruption detectable. However, the algorithm’s reliance on modular addition and fixed round functions also introduces weaknesses: collisions become statistically more likely over time, especially with targeted attacks.
Table of Contents
- The Complete Overview of What Is an MD5 Checksum
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Is MD5 still safe to use for password storage?
- Q: Why do some software vendors still provide MD5 checksums?
- Q: Can MD5 be used to detect file tampering?
- Q: How does MD5 compare to CRC32 for file verification?
- Q: Are there any legal or compliance risks associated with using MD5?
- Q: Can I generate an MD5 checksum without specialized tools?
- Q: What’s the difference between MD5 and SHA-1?
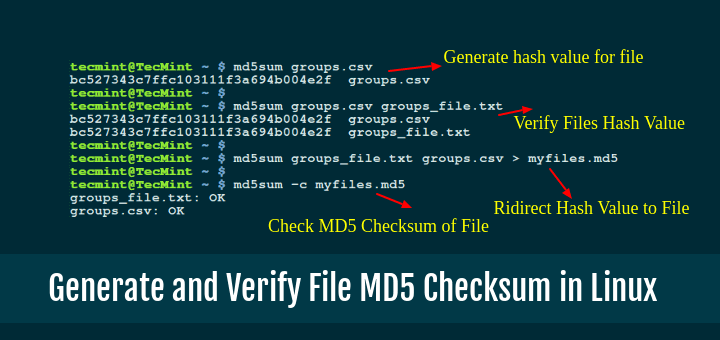
The practical workflow for using MD5 is straightforward:
1. Generate the hash: Feed the file through the MD5 function (e.g., via `md5sum` in Linux or `certutil` in Windows).
2. Compare: Match the generated hash against a known-good reference (e.g., a checksum provided by a software vendor).
3. Verify: If they match, the file is intact; if not, corruption or tampering has occurred.
Key Benefits and Crucial Impact
The enduring relevance of what is an MD5 checksum lies in its ability to solve a fundamental problem in digital systems: how do you trust that data hasn’t changed? In an era where files traverse untrusted networks, MD5 provides a lightweight, deterministic answer. Its speed—processing data at rates of hundreds of MB/s—makes it ideal for scenarios where performance matters more than cryptographic perfection. For example, in peer-to-peer file sharing (like BitTorrent), MD5 hashes are used to verify partial downloads before stitching them together. Similarly, in software distribution, vendors often publish MD5 checksums alongside ISOs or executables, allowing users to validate their downloads against known-good hashes.Yet the impact of MD5 extends beyond technical utility. It’s a case study in the trade-offs between security and practicality. While MD5 is not secure against malicious attacks, its speed and simplicity make it indispensable for non-critical integrity checks. This dichotomy has led to a bifurcated use case: MD5 thrives in environments where accidental corruption is the primary concern (e.g., backups, log files), while stronger hashes like SHA-256 dominate in security-sensitive contexts (e.g., password storage, blockchain). The algorithm’s legacy also highlights a broader truth: even "broken" cryptographic tools can serve niche purposes, provided their limitations are understood.
"MD5 is like a speedometer in a race car: it tells you how fast you’re going, but it won’t stop a crash. Use it wisely, and it’s invaluable; ignore its flaws, and you’re asking for trouble." — Bruce Schneier, Cryptographer and Security Expert
Major Advantages
The persistence of what is an MD5 checksum in modern systems stems from its five key advantages:- Blazing Speed: MD5 processes data at near-linear speeds, making it ideal for large files or high-throughput systems. A 1GB file can be hashed in under a second on modern hardware.
Comparative Analysis
While what is an MD5 checksum remains useful in specific contexts, its limitations have spurred the development of stronger alternatives. Below is a comparison of MD5 against other hash functions:| Criteria | MD5 | SHA-1 | SHA-256 | BLAKE3 |
|---|---|---|---|---|
| Output Size (bits) | 128 | 160 | 256 | 256 |
| Collision Resistance | Weak (broken by 2004) | Weak (deprecated by 2011) | Strong (currently secure) | Strong (modern, optimized) |
| Speed (MB/s on modern CPU) | ~500–1,000 | ~300–600 | ~200–400 | ~900–1,200 |
| Primary Use Case | Non-security checksums | Legacy systems | Security (SSL, blockchain) | High-speed integrity |
Future Trends and Innovations
The future of what is an MD5 checksum is one of gradual phase-out, replaced by stronger but more computationally intensive algorithms. SHA-3 (Keccak) and BLAKE3 are already challenging SHA-256’s dominance, offering better collision resistance and hardware acceleration. However, MD5 isn’t disappearing entirely—it persists in legacy systems, embedded devices, and scenarios where minimal overhead is critical. The rise of post-quantum cryptography may also reshape hashing: algorithms like SPHINCS+ or XMSS, designed to resist attacks from quantum computers, could render MD5 obsolete even for non-security uses by 2030.One emerging trend is the hybrid approach: systems using MD5 for initial integrity checks (due to speed) and then applying a stronger hash (e.g., SHA-3) for critical operations. For example, a firmware update might first verify its MD5 checksum to catch corruption, then use a SHA-256 signature to authenticate its source. This layered defense reflects a pragmatic evolution: what is an MD5 checksum isn’t dead, but it’s being repurposed—like a Swiss Army knife, still useful for some tasks, but no longer the go-to tool for everything.

Conclusion
MD5’s story is a microcosm of cryptography’s evolution: a tool born of necessity, celebrated for its elegance, and eventually outgrown by reality. What is an MD5 checksum is more than a technical specification—it’s a lesson in balancing trade-offs. Its speed and simplicity made it indispensable for decades, but its collision vulnerabilities forced a reckoning. Today, the algorithm serves as a reminder that security isn’t static; it’s a moving target shaped by advancements in both hardware and cryptanalysis. As industries migrate to SHA-3 and beyond, MD5’s legacy endures not as a relic, but as a cautionary example of how even the most ubiquitous tools can become obsolete when their limitations are exposed.For practitioners, the takeaway is clear: understand the context. MD5 is still valid for detecting accidental corruption in non-security-critical applications, but it’s no substitute for SHA-256 in scenarios involving authentication or digital signatures. The future belongs to algorithms that can adapt—whether through quantum resistance or hardware optimization—but MD5’s place in history is secure as a foundational building block of modern data integrity.
Comprehensive FAQs
Q: Is MD5 still safe to use for password storage?
A: No. MD5 is never recommended for password storage due to its vulnerability to rainbow table attacks and collision weaknesses. Modern systems use algorithms like bcrypt, Argon2, or PBKDF2, which incorporate salt and computational delays to thwart brute-force attacks.
Q: Why do some software vendors still provide MD5 checksums?
A: Vendors often include MD5 checksums for backward compatibility and simplicity. While MD5 isn’t cryptographically secure, it’s still effective at detecting accidental corruption during downloads or transfers. For critical updates, vendors may also provide SHA-256 hashes alongside MD5 for added security.
Q: Can MD5 be used to detect file tampering?
A: Yes, but with caveats. MD5 can detect accidental changes (e.g., corrupted downloads), but it’s not secure against malicious tampering. If an attacker knows the original hash, they could theoretically craft a file that matches it—though this requires significant computational effort. For tamper-proofing, use digital signatures with RSA or ECDSA.
Q: How does MD5 compare to CRC32 for file verification?
A: MD5 is far more robust than CRC32 (a non-cryptographic checksum). While CRC32 is faster and sometimes used in networking, it’s prone to more collisions (different files producing the same checksum) and doesn’t meet cryptographic standards. MD5, despite its flaws, is still superior for integrity checks in most non-security contexts.
Q: Are there any legal or compliance risks associated with using MD5?
A: In some jurisdictions, using MD5 for cryptographic purposes (e.g., digital signatures) may violate standards like FIPS 180-4, which deprecated it in 2012. Organizations handling sensitive data (e.g., healthcare, finance) should consult compliance guidelines to avoid using MD5 where stronger hashes are required.
Q: Can I generate an MD5 checksum without specialized tools?
A: Yes. Most operating systems include built-in commands:
Q: What’s the difference between MD5 and SHA-1?
A: SHA-1 (160-bit output) was designed to fix MD5’s collision vulnerabilities but was itself broken in 2017. While SHA-1 is stronger than MD5, it’s now considered insecure for most security applications. Both are similar in speed, but SHA-1’s larger output size provides slightly better collision resistance—though neither is suitable for cryptographic security today.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.