What Is an RSA? The Hidden Power Behind Secure Digital Transactions

When you log into your bank account, sign a legally binding document digitally, or browse a secure website, you’re relying on an invisible shield: RSA encryption. This cryptographic workhorse has silently underpinned the internet’s security for decades, yet few outside of cybersecurity circles truly grasp what is an RSA—or why it matters. It’s not just a tool; it’s the bedrock of trust in a digital world where data breaches and identity theft are constant threats.
The acronym RSA stands for Rivest-Shamir-Adleman, named after the MIT mathematicians who invented it in 1977. What makes RSA revolutionary isn’t just its complexity—it’s its elegance. Unlike earlier encryption methods that relied on shared secrets, RSA introduced a radical concept: two keys, one public, one private, where the former could encrypt data but only the latter could decrypt it. This asymmetry transformed how we think about security, enabling everything from HTTPS to blockchain without the need for pre-shared keys.
Yet for all its ubiquity, RSA remains shrouded in mystique. How does it actually work? Why is it still used when quantum computing looms on the horizon? And what happens when someone asks, “What does RSA stand for in cybersecurity?”—a question that reveals deeper gaps in public understanding. This exploration dives into the mathematical foundations, real-world applications, and future challenges of RSA, demystifying the algorithm that keeps the digital world running.
The Complete Overview of RSA Encryption
At its core, RSA is a public-key cryptosystem, meaning it uses a pair of mathematically linked keys: a public key for encryption and a private key for decryption. The genius of RSA lies in its reliance on the computational difficulty of factoring large prime numbers—a problem that, as of 2024, remains intractable for classical computers. When you encounter what is RSA encryption in security documentation, you’re looking at the algorithm that powers everything from SSL/TLS certificates to digital signatures.
The algorithm’s strength stems from its foundation in number theory, specifically Euler’s theorem and the properties of modular arithmetic. Unlike symmetric encryption (where the same key encrypts and decrypts), RSA’s asymmetric approach allows for secure communication without prior key exchange. This innovation was so disruptive that it became the cornerstone of modern cryptographic protocols, including PGP (Pretty Good Privacy) and SSH (Secure Shell). Even today, when developers ask, “What is RSA used for?”, the answer spans authentication, encryption, and non-repudiation.
Historical Background and Evolution
RSA’s origins trace back to 1973, when Whitfield Diffie and Martin Hellman published their seminal paper on public-key cryptography. However, the algorithm itself was independently developed four years later by Ron Rivest, Adi Shamir, and Leonard Adleman at MIT—a collaboration that accidentally led to a patent dispute with the British government, which had classified similar work decades earlier. The irony? The UK’s GCHQ had already cracked the problem in the 1960s but kept it secret.
Table of Contents
- The Complete Overview of RSA Encryption
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What is an RSA in simple terms?
- Q: What is the difference between RSA and SSL/TLS?
- Q: What is an RSA key pair?
- Q: What is RSA used for in real life?
- Q: What is the weakest part of RSA?
- Q: What is the future of RSA?
- Q: Can RSA be hacked?
By the early 1990s, RSA had become the de facto standard for secure communications. The invention of the SSL protocol (later TLS) in 1995 cemented its role in web security, while its adoption in PKI (Public Key Infrastructure) systems ensured that digital certificates—critical for HTTPS—relied on RSA’s integrity. Over time, the algorithm evolved to address vulnerabilities (like the 2010 Bleichenbacher attack on PKCS#1 v1.5 padding), but its core principles remained unchanged. Today, when you see a padlock icon in your browser, you’re witnessing RSA in action—even if you’ve never asked, “What does RSA mean in encryption?”.
Core Mechanisms: How It Works
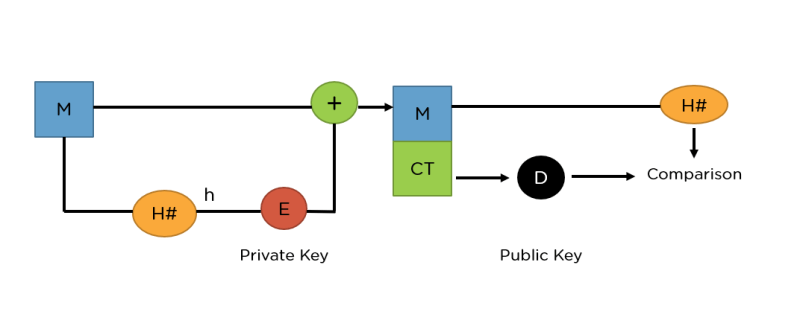
RSA’s operation hinges on three mathematical steps: key generation, encryption, and decryption. First, two large prime numbers (typically 1,024 to 4,096 bits) are selected and multiplied to create a modulus (n). A public exponent (e) is chosen, and its modular inverse (d) becomes the private exponent. The public key (n, e) is shared openly, while the private key (d) remains secret. When data is encrypted using the public key, only the corresponding private key can decrypt it—a process relying on the difficulty of reversing the operation without factoring n.
The algorithm’s security derives from the fact that, while multiplying primes is easy, factoring their product into primes is computationally infeasible for sufficiently large numbers. For example, a 2,048-bit RSA key has roughly 600 digits; factoring it would require more computational power than exists on Earth. This asymmetry is why RSA can securely transmit keys for symmetric encryption (like AES), combining the best of both worlds. When you encounter what is RSA in cryptography, you’re seeing the marriage of pure mathematics and practical security.
Key Benefits and Crucial Impact
RSA’s influence extends beyond theory into tangible benefits: it enables secure authentication, data confidentiality, and legal non-repudiation. Without RSA, modern e-commerce, government communications, and even email encryption (via S/MIME) would be far less secure. The algorithm’s ability to verify identities through digital signatures has made it indispensable in industries where trust is non-negotiable—like finance and healthcare. Yet its impact isn’t just technical; it’s cultural. RSA has redefined how we perceive security, shifting from secrecy to transparency.
The algorithm’s versatility is unmatched. It secures everything from VPNs to Bitcoin transactions, where it authenticates wallet addresses. Even in post-quantum research, RSA remains a benchmark, with variants like RSA-FDH (Full Domain Hash) still under scrutiny. When you ask, “What is the purpose of RSA?”, the answer is simple: to provide a framework where trust is mathematically guaranteed. This isn’t just theory—it’s the invisible infrastructure of the digital age.
—“RSA is the cryptographic equivalent of a Swiss Army knife: compact, reliable, and capable of handling tasks no one else can.”
—Bruce Schneier, Cryptographer and Security Expert
Major Advantages
- Asymmetric Security: Unlike symmetric encryption, RSA doesn’t require pre-shared keys, eliminating the risk of key distribution attacks.
- Digital Signatures: RSA enables non-repudiation, ensuring senders cannot deny sending a message (critical for contracts and legal documents).
- Key Exchange: RSA can securely distribute symmetric keys (e.g., AES keys), combining efficiency with security.
- Scalability: Public keys can be freely distributed, making RSA ideal for large-scale systems like PKI.
- Mathematical Rigor: Its security is based on well-understood number theory, making it resistant to ad-hoc attacks.

Comparative Analysis
While RSA dominates public-key cryptography, other algorithms serve niche roles. Below is a comparison of RSA with its primary alternatives:
| Feature | RSA | Elliptic Curve Cryptography (ECC) | Diffie-Hellman (DH) |
|---|---|---|---|
| Key Size | 2,048-bit ≈ 112-bit security | 256-bit ≈ 112-bit security | 2,048-bit ≈ 112-bit security |
| Use Case | Encryption, signatures, key exchange | Encryption, signatures (smaller keys) | Key exchange only |
| Speed | Slower (modular exponentiation) | td>Faster (point multiplication)Moderate (group operations) | |
| Quantum Vulnerability | Broken by Shor’s algorithm | Broken by Shor’s algorithm | Broken by Shor’s algorithm |
Future Trends and Innovations
RSA’s future is under siege from quantum computing. Shor’s algorithm, when implemented on a large-scale quantum computer, could factor RSA keys in seconds, rendering the algorithm obsolete. This has spurred research into post-quantum cryptography (PQC), where lattice-based and hash-based signatures are gaining traction. However, RSA isn’t dead—it’s being adapted. Hybrid systems (combining RSA with PQC) and longer key lengths (e.g., 4,096-bit RSA) are temporary stopgaps until quantum-resistant alternatives mature.
Beyond quantum threats, RSA’s evolution lies in efficiency. As devices grow more constrained (IoT, edge computing), algorithms like ECC and Kyber (NIST’s PQC finalist) are reducing key sizes without sacrificing security. Yet RSA’s legacy endures in legacy systems, where migration is costly. For now, the question “What is RSA in modern cryptography?” still points to a foundational role—even if its reign is numbered.
Conclusion
RSA is more than an algorithm; it’s a cultural touchstone of the digital age. From securing your morning coffee order on a café’s Wi-Fi to authenticating nuclear launch codes, its impact is invisible yet profound. While newer cryptographic primitives emerge, RSA’s historical significance cannot be overstated. It proved that security could be both mathematical and scalable, paving the way for the internet’s trust infrastructure.
The next decade will test RSA’s resilience. Quantum computing may force its retirement, but its principles will live on in the next generation of cryptographic systems. For now, when you ask “What is RSA encryption used for?”, remember: it’s the silent guardian of a world that demands certainty in an uncertain digital landscape.
Comprehensive FAQs
Q: What is an RSA in simple terms?
A: RSA is a cryptographic system that uses two keys—a public key to encrypt data and a private key to decrypt it. It’s like a digital lock where anyone can send you a message (using your public key), but only you can open it (with your private key).
Q: What is the difference between RSA and SSL/TLS?
A: RSA is the algorithm that enables key exchange and digital signatures in SSL/TLS. SSL/TLS is the protocol that uses RSA (along with other cryptographic tools) to secure communications between servers and clients (e.g., your browser and a website).
Q: What is an RSA key pair?
A: An RSA key pair consists of a public key (shared openly) and a private key (kept secret). The public key can encrypt data or verify signatures, while the private key decrypts data or creates signatures. Both keys are mathematically linked but cannot be derived from each other.
Q: What is RSA used for in real life?
A: RSA secures:
- HTTPS websites (via TLS certificates)
- Digital signatures (e.g., code signing, email authentication)
- VPNs and secure remote access
- Blockchain transactions (e.g., Bitcoin address generation)
- Secure email (S/MIME, PGP)
Q: What is the weakest part of RSA?
A: RSA’s primary vulnerability is its reliance on the difficulty of factoring large primes. Weaknesses include:
- Small key sizes (e.g., 512-bit RSA is now considered broken)
- Poor random number generation in key creation
- Side-channel attacks (e.g., timing attacks on implementations)
- Quantum computing (Shor’s algorithm can break RSA)
Q: What is the future of RSA?
A: RSA’s future hinges on post-quantum cryptography. While hybrid systems (combining RSA with PQC algorithms) may extend its lifespan, long-term security will require migration to quantum-resistant alternatives like:
- Lattice-based cryptography (e.g., Kyber, Dilithium)
- Hash-based signatures (e.g., SPHINCS+)
- Code-based cryptography (e.g., McEliece)
Q: Can RSA be hacked?
A: Yes, but only under specific conditions:
- Brute-force attacks (impractical for 2,048+ bit keys)
- Mathematical breakthroughs (e.g., a factoring algorithm faster than general-purpose methods)
- Implementation flaws (e.g., weak randomness, side-channel leaks)
- Quantum computers (Shor’s algorithm would make RSA obsolete) For now, properly configured RSA remains secure against classical attacks.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.