Beyond the Hype: A Reality Check on Security Risks Protection
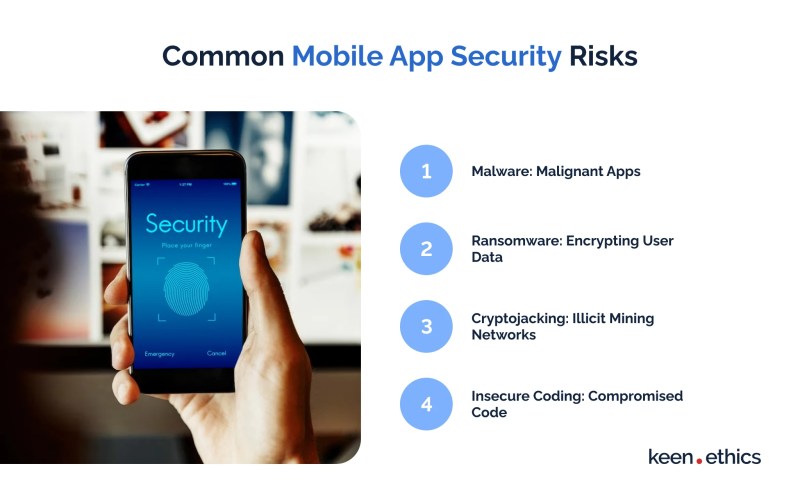
The illusion of absolute security is a myth perpetuated by vendors and marketers. Every system, protocol, and "unbreakable" encryption has a weak point—whether it’s a zero-day exploit, human error, or systemic oversight. The reality check on security risks protection reveals that no solution is foolproof, but understanding these vulnerabilities is the first step toward meaningful defense. What’s often sold as impenetrable security is, in truth, a series of calculated trade-offs between convenience, cost, and resilience.
Corporations, governments, and individuals alike operate under the assumption that their security measures are sufficient—until they’re not. A single misconfigured firewall, an unpatched vulnerability, or a phishing email can dismantle years of investment in security infrastructure. The gap between perceived protection and actual risk exposure is widening, and the consequences of this disconnect are severe: data breaches, financial losses, reputational damage, and even physical harm in critical infrastructure scenarios. The question isn’t whether security risks protection will fail; it’s when and how badly.
Yet, the conversation around security often remains abstract, detached from the harsh realities of implementation. Vendors emphasize features like "AI-driven threat detection" or "quantum-resistant encryption," but the cold truth is that these tools are only as effective as the humans deploying them—and human factors remain the weakest link. This article cuts through the noise to deliver a grounded assessment of security risks protection, exploring its mechanisms, limitations, and the strategic adjustments needed to align defenses with evolving threats.
The Complete Overview of Reality Check Security Risks Protection
Security risks protection isn’t a monolithic concept but a dynamic interplay of technology, policy, and human behavior. At its core, it represents the deliberate effort to identify, mitigate, and respond to threats in a way that reflects their actual probability and impact—not just theoretical worst-case scenarios. The challenge lies in balancing overprotection (which stifles productivity) with underprotection (which invites exploitation). The reality check begins with acknowledging that no system is immune to failure; the goal, then, is to fail safely—minimizing damage when breaches occur rather than assuming they can be prevented entirely.The modern landscape of security risks protection is fragmented. Enterprises deploy layered defenses—firewalls, endpoint detection, multi-factor authentication (MFA), and zero-trust architectures—yet these layers often operate in silos, creating blind spots. Meanwhile, attackers exploit the friction between these systems, leveraging social engineering, supply chain vulnerabilities, or even insider threats to bypass technical controls. The result is a paradox: organizations spend billions on security tools, yet the frequency and sophistication of attacks continue to rise. This disconnect stems from a fundamental misalignment between how security is marketed and how it’s practiced.
Historical Background and Evolution
The evolution of security risks protection traces back to the early days of computing, when physical access controls and rudimentary password policies were the primary defenses. As networks expanded in the 1980s and 1990s, so did the need for firewalls and intrusion detection systems (IDS). These early measures were reactive, designed to block known threats rather than anticipate emerging ones. The turn of the millennium brought the rise of antivirus software and perimeter security, but by the 2000s, attackers had already moved beyond simple malware to exploit application-layer vulnerabilities and human psychology.The post-9/11 era accelerated the militarization of cybersecurity, with governments and corporations investing heavily in classified threat intelligence and encryption standards. However, this period also highlighted a critical flaw: security measures became increasingly complex, requiring specialized expertise to manage. The gap between what security professionals could implement and what average users understood grew wider, creating opportunities for attackers to exploit confusion and complacency. By the 2010s, the shift to cloud computing and remote work further complicated the equation, as traditional perimeter defenses became obsolete in favor of identity-centric and device-agnostic security models.
Table of Contents
- The Complete Overview of Reality Check Security Risks Protection
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do I know if my current security measures are sufficient?
- Q: Can small businesses afford robust security risks protection?
- Q: What’s the biggest misconception about security risks protection?
- Q: How often should security policies be updated?
- Q: Is encryption enough to protect against all security risks?
Today, the security risks protection paradigm is defined by three overlapping trends: the proliferation of connected devices (IoT), the rise of state-sponsored cyber warfare, and the democratization of hacking tools. What was once the domain of nation-states or organized crime is now accessible to lone actors with minimal technical skills. This democratization has forced security professionals to reconsider their strategies, moving from static defenses to adaptive, intelligence-driven approaches. Yet, despite these advancements, the fundamental truth remains: security risks protection is not about eliminating risk but managing it within acceptable parameters.
Core Mechanisms: How It Works
The mechanics of security risks protection revolve around three pillars: prevention, detection, and response. Prevention involves deploying technical controls—such as encryption, access restrictions, and secure coding practices—to reduce the attack surface. However, prevention alone is insufficient because no system can account for every possible threat vector. This is where detection comes into play, utilizing tools like SIEM (Security Information and Event Management) systems, anomaly detection algorithms, and threat intelligence feeds to identify suspicious activity in real time.The final pillar, response, is often the most overlooked. Even the most robust detection systems can miss threats, and when they do, the ability to contain and recover from an incident determines the severity of the outcome. Incident response plans (IRPs) outline the steps to isolate affected systems, preserve evidence, and restore operations while minimizing downtime. Yet, many organizations treat response as an afterthought, only to face chaos when a breach occurs. The reality check here is stark: the effectiveness of security risks protection hinges on how well an organization can react—not just how well it can prevent.
Underlying these mechanisms is the principle of defense in depth, which advocates for layered security controls to ensure that if one layer fails, others remain intact. However, depth alone doesn’t guarantee success; the layers must be cohesive. For example, a zero-trust architecture requires not just network segmentation but also continuous authentication and least-privilege access policies. Without alignment between technical controls and organizational policies, gaps inevitably emerge, leaving systems vulnerable to exploitation.
Key Benefits and Crucial Impact
The primary benefit of a disciplined approach to security risks protection is risk reduction—not elimination, but the minimization of exposure to critical threats. When implemented correctly, these measures can prevent financial losses, protect sensitive data, and maintain operational continuity. For businesses, this translates to reduced insurance premiums, regulatory compliance, and customer trust. Governments and critical infrastructure operators rely on security risks protection to safeguard national security and public safety, as seen in sectors like energy, healthcare, and transportation.Yet, the impact of security risks protection extends beyond tangible outcomes. A well-structured security posture fosters a culture of awareness, where employees recognize their role in maintaining resilience. This cultural shift is often the most durable defense against evolving threats, as it turns passive users into active participants in security. The downside, however, is that overemphasis on security can create friction—slowing down legitimate workflows, increasing costs, and frustrating end-users. Striking the right balance between security and usability is the crux of effective risk management.
> "Security is not a product, but a process. The best systems are those that evolve with the threats they face, not those that rely on static rules." — Bruce Schneier, Security Technologist
Major Advantages
- Proactive Threat Mitigation: Advanced threat intelligence and predictive analytics allow organizations to identify and neutralize risks before they materialize into breaches.
- Regulatory Compliance: Adhering to frameworks like ISO 27001, NIST, or GDPR reduces legal exposure and avoids costly penalties for non-compliance.
- Resilience Against Insider Threats: Role-based access controls and behavioral analytics help detect and prevent malicious or negligent actions from within the organization.
- Cost Efficiency in the Long Run: While initial investments in security infrastructure are high, the cost of a single breach—averaging millions in damages—far outweighs proactive spending.
- Enhanced Reputation Management: Organizations that demonstrate robust security risks protection are more likely to retain customers, attract partners, and secure funding.
Comparative Analysis
| Traditional Security Models | Modern Adaptive Security |
|---|---|
| Relies on static perimeter defenses (firewalls, VPNs). | Employs dynamic, identity-centric access (zero trust, MFA). |
| Focuses on known threats (signature-based detection). | Uses AI/ML for anomaly detection and behavioral analysis. |
| Assumes trust within the network ("castle-and-moat" model). | Operates on "never trust, always verify" principles. |
| Reactively responds to breaches post-incident. | Implements automated incident response and continuous monitoring. |
Future Trends and Innovations
The next frontier in security risks protection lies in automation and AI-driven resilience. Machine learning algorithms are increasingly capable of predicting attack patterns, while autonomous response systems can contain threats in seconds. However, this automation introduces new challenges, particularly around explainability—organizations must ensure that AI-driven decisions are transparent and auditable to avoid introducing new risks.Another emerging trend is quantum-resistant cryptography, as quantum computing threatens to obsolete current encryption standards. Governments and tech giants are already investing in post-quantum algorithms, but widespread adoption remains years away. Meanwhile, biometric authentication is becoming more sophisticated, moving beyond fingerprints to behavioral biometrics like typing patterns or gait analysis. These innovations promise stronger authentication but also raise privacy concerns, particularly as biometric data becomes a new target for attackers.
The most critical trend, however, is the human element. As technology advances, the weakest link remains people—whether through phishing, social engineering, or misconfigured systems. Future security risks protection strategies will increasingly focus on security awareness training, gamification of learning, and psychological resilience to counter human vulnerabilities. The organizations that succeed will be those that treat security not as an IT issue but as a cultural imperative.

Conclusion
The reality check on security risks protection is simple: no system is invincible, but the right combination of technology, policy, and human vigilance can significantly reduce exposure. The illusion of absolute security is a dangerous myth; the goal should be resilient security—one that acknowledges failure as a possibility and prepares for it accordingly. This requires a shift from reactive measures to proactive, adaptive strategies that evolve with threats.For individuals and organizations alike, the path forward lies in continuous assessment, investment in emerging technologies, and a commitment to security as an ongoing process—not a one-time solution. The stakes are too high to rely on outdated assumptions or vendor hype. By confronting the harsh realities of security risks protection, we can build defenses that are not just strong on paper but effective in practice.
Comprehensive FAQs
Q: How do I know if my current security measures are sufficient?
A: Conduct a penetration test or red team exercise to identify vulnerabilities. Additionally, perform a risk assessment aligned with frameworks like NIST or ISO 27001 to evaluate gaps. If your defenses rely solely on traditional perimeter security (e.g., firewalls), they’re likely outdated—modern threats require zero-trust architectures and continuous monitoring.
Q: Can small businesses afford robust security risks protection?
A: Yes, but prioritization is key. Start with multi-factor authentication (MFA), endpoint protection, and employee training—these offer the highest ROI. Managed security services (MSSPs) can provide affordable, scalable solutions tailored to smaller budgets. The cost of not protecting against breaches (e.g., ransomware, data leaks) far exceeds proactive spending.
Q: What’s the biggest misconception about security risks protection?
A: The belief that more technology equals better security. Many organizations pile on tools without integrating them, creating complexity and blind spots. Effective security risks protection requires cohesive layers, not just more firewalls or antivirus software. Human error and poor policies often outweigh technical failures.
Q: How often should security policies be updated?
A: At least annually, or whenever major changes occur (e.g., new regulations, mergers, remote work policies). Threat landscapes evolve rapidly—what was secure last year may be obsolete today. Automated compliance tools can help track changes, but manual reviews by security teams are essential to ensure policies align with real-world risks.
Q: Is encryption enough to protect against all security risks?
A: No. Encryption secures data in transit and at rest, but it doesn’t protect against social engineering, misconfigured systems, or insider threats. A comprehensive security risks protection strategy must combine encryption with access controls, threat detection, and incident response planning to address all attack vectors.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.