How Remote Work’s Security Risks Evolve—And Why Features Can’t Keep Up

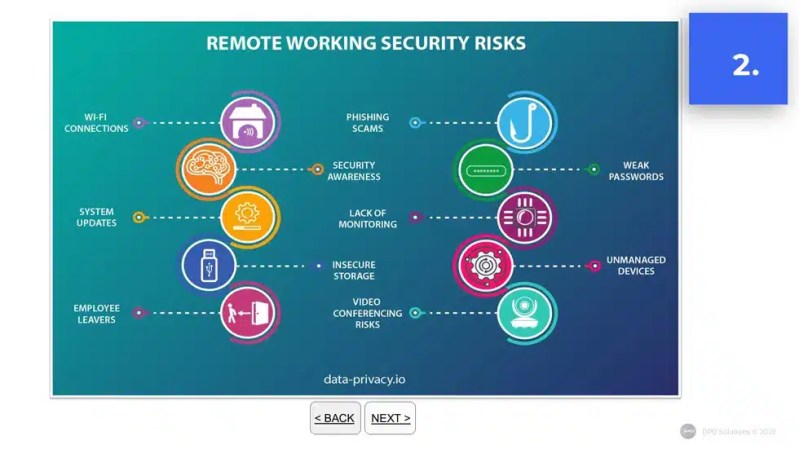
The shift to remote work didn’t just redefine productivity—it fractured the perimeter. Overnight, corporate networks became porous, with employees accessing sensitive data from unmanaged devices, public Wi-Fi, and cloud apps with inconsistent security controls. What began as a temporary adaptation became permanent, and with it, a relentless arms race between cybercriminals exploiting new attack surfaces and security teams scrambling to adapt. The features security risks evolution remote dynamic isn’t linear; it’s a feedback loop where each innovation—from zero-trust architectures to AI-driven threat detection—spawns fresh vulnerabilities.
The problem isn’t just the volume of risks. It’s their velocity. In 2020, phishing attacks surged 667% as remote workers fell victim to impersonation schemes. By 2023, ransomware groups like LockBit were targeting unpatched VPNs and misconfigured cloud storage, while insider threats—often unintentional—rose due to blurred lines between personal and professional data. Security features designed for office-bound environments (like network segmentation or on-premise firewalls) became obsolete when endpoints moved outside controlled IT ecosystems. The evolution of remote security risks isn’t just about more threats; it’s about threats that evolve faster than the defenses meant to stop them.
What’s missing isn’t better tools—it’s a fundamental rethinking of how security features align with remote work’s realities. Legacy systems treat risks as static; modern threats are dynamic. The gap between what security teams can monitor and what attackers can exploit is widening, and the cost isn’t just financial. It’s reputational, operational, and—when critical infrastructure is compromised—even physical.
The Complete Overview of Remote Security Risks and Their Evolution
The features security risks evolution remote narrative is one of constant reinvention. What started as isolated incidents—like the 2003 SQL Slammer worm exploiting unpatched home networks—has morphed into a systemic crisis. Today, remote work isn’t just a vector for cyberattacks; it’s a catalyst for entirely new threat models. The traditional triad of confidentiality, integrity, and availability (CIA) now faces a fourth challenge: context—understanding where data resides, who accesses it, and under what conditions. Security features that once relied on static rules (e.g., "block all traffic from outside the LAN") now require real-time, behavioral analysis to distinguish between a legitimate employee and a compromised device.The paradox is that the same technologies enabling remote work—cloud services, BYOD policies, and SaaS applications—are also the weakest links. Features designed for convenience (like single sign-on or file-sharing tools) often prioritize usability over security, creating blind spots. For example, a 2022 study by IBM found that 83% of organizations experienced more than one cloud data breach, with misconfigured storage buckets being the top cause. The evolution of remote security risks isn’t just about hackers; it’s about the unintended consequences of well-meaning but poorly secured features.
Historical Background and Evolution
The roots of remote security risks trace back to the 1990s, when dial-up modems and early VPNs introduced the first "remote access" vulnerabilities. Early exploits targeted weak encryption or stolen credentials, but the scale was limited. Fast-forward to the 2010s, and the rise of bring-your-own-device (BYOD) policies turned employee smartphones into corporate liabilities. Mobile device management (MDM) solutions emerged as a response, but they were reactive—locking down devices after breaches occurred rather than preventing them.The pandemic accelerated this evolution exponentially. Overnight, IT departments had to secure endpoints they couldn’t touch, enforce policies on devices they didn’t own, and monitor traffic flowing through ISPs they couldn’t control. Features like endpoint detection and response (EDR) became essential, but their effectiveness hinged on one critical factor: visibility. Without a unified view of remote networks, security teams were flying blind. The features security risks evolution remote timeline isn’t just a chronology of attacks; it’s a story of how each security feature—from firewalls to zero-trust—was forced to adapt or become obsolete.
Core Mechanisms: How It Works
At its core, the evolution of remote security risks revolves around three interconnected mechanisms: exposure, exploitation, and escalation. Exposure occurs when remote work eliminates physical controls (e.g., badge access, on-site IT oversight). Exploitation happens when attackers identify and abuse weaknesses in security features—like unpatched software, weak authentication, or shadow IT. Escalation is where isolated incidents become systemic, often through lateral movement within compromised networks.Table of Contents
- The Complete Overview of Remote Security Risks and Their Evolution
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: How do remote security risks differ from traditional office-based threats?
- Q: What’s the biggest misconception about remote security features?
- Q: Can small businesses afford advanced remote security features?
- Q: How often should security features be updated for remote work?
- Q: What’s the most underrated remote security risk?
Take the case of ransomware in 2021. Attackers exploited unsecured RDP ports, weak passwords, and unmonitored remote desktop sessions to infiltrate networks. The features security risks evolution remote dynamic here is telling: traditional perimeter defenses (like next-gen firewalls) couldn’t stop attacks originating from inside the network. The solution? Zero-trust architectures, which assume breach and verify every access request—regardless of location. Yet even zero-trust isn’t foolproof. Misconfigured identity providers or over-permissive access policies can create new attack surfaces.
Key Benefits and Crucial Impact
Remote work’s security risks aren’t just a technical challenge; they’re a strategic one. Organizations that fail to address the features security risks evolution remote gap risk more than data breaches—they risk eroding trust, compliance violations, and regulatory fines. The impact extends beyond IT: HR faces reputational damage from leaked employee data, legal teams grapple with GDPR or CCPA violations, and executives contend with shareholder lawsuits over negligence.The silver lining? Proactive security features—like behavioral analytics, automated patch management, and AI-driven threat hunting—can mitigate risks before they materialize. The challenge lies in balancing security with productivity. Features like conditional access or device posture checks slow down users, creating friction that often leads to workarounds (e.g., disabling security prompts). The evolution of remote security risks demands a shift from "block everything" to "trust but verify"—but execution requires cultural change as much as technological investment.
"Security isn’t about stopping every attack. It’s about reducing the attack surface to the point where the cost of exploitation exceeds the value of the target." — Mikko Hypponen, Chief Research Officer at F-Secure
Major Advantages
Despite the risks, addressing the features security risks evolution remote landscape offers tangible benefits:- Reduced Attack Surface: Zero-trust models and micro-segmentation limit lateral movement, containing breaches before they spread.
- Automated Compliance: Features like continuous monitoring and automated policy enforcement help meet regulatory requirements (e.g., HIPAA, PCI DSS) without manual audits.
- Proactive Threat Detection: AI-driven tools analyze user behavior in real-time, flagging anomalies like data exfiltration or unauthorized access attempts.
- Scalable Security: Cloud-based security features (e.g., CASBs, SWG) adapt to fluctuating remote workforces without hardware upgrades.
- User Awareness Integration: Security features tied to training (e.g., phishing simulations, secure password managers) reduce human error—the leading cause of breaches.

Comparative Analysis
| Security Feature | Strengths | Weaknesses ||----------------------------|----------------------------------------|-----------------------------------------|
| Zero-Trust Architecture | Minimizes lateral movement, reduces over-permissive access | High implementation cost, complex policy management |
| Endpoint Detection & Response (EDR) | Real-time threat hunting, automated containment | Requires agent deployment, false positives |
| Cloud Access Security Broker (CASB) | Monitors SaaS apps, enforces DLP policies | Limited to cloud traffic, bypass risks |
| Multi-Factor Authentication (MFA) | Reduces credential theft impact | User fatigue, phishing-resistant MFA needed |
Future Trends and Innovations
The next phase of the features security risks evolution remote will be shaped by three forces: AI, quantum computing, and regulatory pressure. AI-driven attacks—like deepfake phishing or autonomous ransomware—will force security features to adopt predictive analytics. Quantum computing, while still nascent, threatens to break encryption standards, prompting a shift to post-quantum cryptography. Meanwhile, regulations like the EU’s NIS2 Directive will impose stricter remote work security mandates, pushing organizations to adopt standardized frameworks.Innovations like continuous authentication (beyond passwords) and homomorphic encryption (processing data without decrypting it) could redefine security features. However, the biggest challenge won’t be technology—it’ll be human behavior. As remote work persists, the evolution of security risks will hinge on whether organizations can move from reactive patching to proactive resilience.
Conclusion
The features security risks evolution remote isn’t a bug—it’s a feature of the modern digital ecosystem. Remote work has permanently altered the threat landscape, and security teams must treat adaptation as a continuous process, not a one-time project. The features that once protected networks are now liabilities if they’re not dynamically updated to match remote realities.The path forward requires three things: visibility (knowing where data lives and who accesses it), agility (updating security features faster than threats evolve), and collaboration (bridging IT, HR, and executive alignment). Ignore these, and the cost of inaction will be measured in more than just dollars—it’ll be measured in lost trust, operational paralysis, and the irreversible damage of a breach.
Comprehensive FAQs
Q: How do remote security risks differ from traditional office-based threats?
The primary difference lies in attack surfaces. Traditional threats target controlled networks with defined perimeters (e.g., firewalls, VPNs). Remote risks exploit unmanaged devices, public Wi-Fi, and cloud misconfigurations, often through social engineering (e.g., phishing) or unpatched software. The evolution of remote security risks also introduces persistent threats, like ransomware that encrypts data on endpoints outside corporate oversight.
Q: What’s the biggest misconception about remote security features?
The biggest myth is that deploying security tools is enough. Many organizations assume features like firewalls or antivirus will stop remote threats, but these are reactive measures. The features security risks evolution remote shows that proactive strategies—like zero-trust, behavioral analytics, and continuous monitoring—are critical. Tools alone can’t compensate for misconfigurations, poor user training, or outdated policies.
Q: Can small businesses afford advanced remote security features?
Not all advanced features require enterprise budgets. Solutions like open-source EDR tools (e.g., Wazuh), cloud-based CASBs (e.g., Netskope), or MFA providers (e.g., Duo Security) offer scalable options. The key is prioritizing high-impact, low-cost measures, such as:
- Enforcing MFA for all remote access
- Using password managers to eliminate credential reuse
- Implementing endpoint encryption for laptops
- Training employees on phishing via simulated attacks
The evolution of remote security risks means even SMBs must adopt a defense-in-depth approach, but it doesn’t require breaking the bank.
Q: How often should security features be updated for remote work?
Security features for remote work should follow a continuous update cycle, not an annual patch schedule. Critical updates (e.g., OS patches, encryption protocols) should be applied within 48 hours of release. Features like:
- Zero-trust policies (e.g., conditional access rules)
- Threat detection algorithms (e.g., AI models)
- Compliance frameworks (e.g., GDPR data mapping)
should be reviewed quarterly or after major incidents (e.g., a breach or new exploit). The features security risks evolution remote proves that static security is obsolete—threats move faster than most organizations can react.
Q: What’s the most underrated remote security risk?
The most overlooked risk is third-party vendor exposure. Remote work relies on SaaS tools, contractors, and freelancers—all of which can introduce vulnerabilities. For example:
- A misconfigured vendor’s cloud storage exposing customer data (e.g., the 2020 Twitter breach via a compromised internal tool)
- Contractors using personal devices with weak security, creating backdoors into corporate networks
- Supply chain attacks targeting remote workers’ devices (e.g., malware-laced updates from a "trusted" vendor)
The evolution of remote security risks increasingly centers on extended attack surfaces, making third-party risk management a non-negotiable priority.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.