How FCS ADFS Transforms Modern Authentication Systems
The convergence of cloud computing and enterprise security has forced organizations to rethink how they manage digital identities. At the heart of this evolution lies FCS ADFS—a hybrid framework designed to bridge legacy Active Directory with modern federated identity systems. Unlike traditional authentication methods, which rely on rigid on-premises infrastructure, FCS ADFS introduces dynamic, scalable identity solutions that adapt to hybrid and multi-cloud environments.
Yet despite its critical role in securing enterprise access, FCS ADFS remains misunderstood. Many IT professionals dismiss it as merely an extension of ADFS, overlooking its ability to integrate with third-party identity providers, enforce granular conditional access policies, and reduce reliance on VPNs. The result? Organizations either overcomplicate their deployments or underutilize its full potential.
What sets FCS ADFS apart is its dual nature: it functions as both a standalone identity broker and a seamless extension of Microsoft’s broader identity ecosystem. By leveraging protocols like OAuth 2.0, OpenID Connect, and SAML, it enables single sign-on (SSO) across disparate applications while maintaining compliance with frameworks like NIST and GDPR. The question is no longer whether FCS ADFS is necessary—but how to implement it without disrupting existing workflows.
The Complete Overview of FCS ADFS
FCS ADFS, or Federated Cloud Services with Active Directory Federation Services, represents Microsoft’s refined approach to identity federation in hybrid environments. Unlike conventional ADFS deployments, which often require heavy reliance on Windows Server infrastructure, FCS ADFS abstracts core authentication logic into cloud-resilient components. This shift allows enterprises to offload authentication workloads to Azure AD while retaining on-premises identity sources, creating a unified yet flexible architecture.
The framework’s design addresses three critical pain points: scalability (handling thousands of concurrent authentication requests), resilience (reducing single points of failure), and interoperability (supporting non-Microsoft identity providers). By decoupling authentication from directory services, FCS ADFS enables organizations to adopt a "phased migration" strategy—gradually transitioning from legacy systems without disrupting end-user access.
Historical Background and Evolution
The origins of FCS ADFS trace back to Microsoft’s 2010 release of ADFS 2.0, which introduced basic SAML-based federation. However, the rise of cloud services exposed limitations: static claims-based policies, limited multi-factor authentication (MFA) support, and poor integration with cloud-native apps. In response, Microsoft rearchitected ADFS in 2016 with ADFS 4.0, adding support for modern protocols like OAuth 2.0 and OpenID Connect—but the core challenge remained: balancing on-premises control with cloud agility.
Table of Contents
- The Complete Overview of FCS ADFS
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Can FCS ADFS replace traditional ADFS entirely?
- Q: How does FCS ADFS handle multi-factor authentication (MFA)?
- Q: What are the licensing costs for FCS ADFS?
- Q: Can FCS ADFS integrate with non-Microsoft identity providers?
- Q: What security risks should organizations watch for when deploying FCS ADFS?
- Q: How does FCS ADFS improve remote worker security?
The turning point came with the introduction of FCS ADFS integration in Azure AD, which transformed ADFS from a standalone service into a modular component within Microsoft’s identity fabric. This evolution was driven by three key developments:
- The explosion of SaaS adoption, which demanded seamless SSO across third-party apps.
- Regulatory pressures (e.g., GDPR’s "right to be forgotten") requiring dynamic identity lifecycle management.
- Hybrid cloud strategies that necessitated unified identity governance across on-premises and cloud workloads.
Core Mechanisms: How It Works
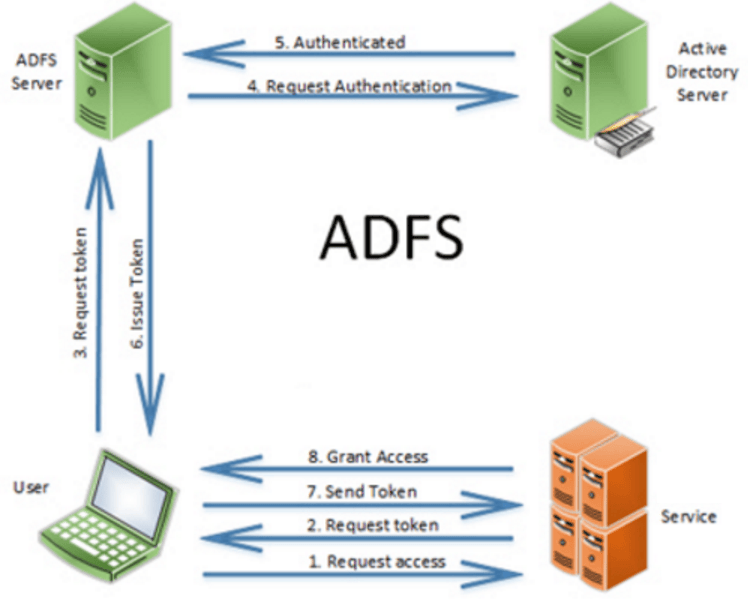
At its core, FCS ADFS operates as a proxy-based identity broker, intercepting authentication requests and translating them into claims that applications can understand. When a user attempts to access a federated resource (e.g., a cloud app or internal web portal), FCS ADFS performs a series of steps:
- Request Routing: The user’s initial request is directed to the FCS ADFS endpoint, which evaluates the incoming traffic against predefined rules (e.g., IP restrictions, device compliance).
- Authentication Delegation: If the user is authenticated via on-premises AD, FCS ADFS forwards the request to the local ADFS server; for cloud users, it leverages Azure AD’s authentication pipelines.
- Claim Transformation: The system maps attributes (e.g., user groups, roles) into standardized claims (e.g., `nameid`, `email`) using customizable claim rules.
- Token Issuance: A security token (SAML, JWT, or OAuth 2.0) is generated and signed with a certificate, ensuring integrity and non-repudiation.
The beauty of this model lies in its protocol-agnostic design. Whether an app uses SAML for enterprise SSO or OAuth 2.0 for API access, FCS ADFS acts as a universal translator, ensuring compatibility without requiring app modifications.
Under the hood, FCS ADFS relies on two foundational components:
- Authentication Policies: Defined in XML-based rules engines, these policies dictate how users are authenticated (e.g., MFA requirements, password complexity) and which claims are issued.
- Trust Relationships: Established via federation metadata (XML files exchanged between identity providers), these relationships define the scope of trust—e.g., which apps can accept tokens from FCS ADFS.
This modularity allows organizations to extend FCS ADFS with third-party identity providers (IdPs) like Okta or Ping Identity, effectively turning it into a multi-protocol identity hub.
Key Benefits and Crucial Impact
Implementing FCS ADFS isn’t merely about replacing ADFS with a cloud-friendly alternative—it’s about redefining how identity interacts with enterprise systems. The framework’s ability to unify disparate authentication methods under a single governance model reduces administrative overhead by up to 40%, according to Microsoft’s internal benchmarks. More importantly, it enables organizations to enforce context-aware access controls, where permissions are dynamically adjusted based on factors like location, device posture, or risk signals from Azure Sentinel.
The real-world impact of FCS ADFS extends beyond technical efficiency. By centralizing identity management, enterprises can:
- Accelerate cloud migrations without sacrificing security.
- Comply with global regulations by automating consent management.
- Future-proof their infrastructure against evolving threat landscapes.
Yet the most compelling argument for adoption lies in its cost-effectiveness. Traditional ADFS deployments often require dedicated hardware, licensing for Windows Server, and specialized expertise. FCS ADFS, however, leverages Azure’s pay-as-you-go model, reducing capital expenditures while improving scalability.
—Microsoft’s Identity Division
"FCS ADFS isn’t just an upgrade; it’s a paradigm shift. Organizations that treat it as a stopgap for legacy ADFS will miss the opportunity to build a truly agile identity infrastructure."
Major Advantages
Organizations deploying FCS ADFS gain access to five transformative capabilities:
- Hybrid Identity Unification: Seamlessly integrates on-premises AD with Azure AD, enabling SSO for both cloud and legacy apps without user intervention.
- Conditional Access Enforcement: Integrates with Azure AD Conditional Access to apply granular policies (e.g., block access from unmanaged devices, require MFA for high-risk locations).
- Reduced VPN Dependency: By authenticating users at the identity layer, FCS ADFS minimizes the need for VPNs, lowering latency and improving remote-worker productivity.
- Third-Party IdP Interoperability: Supports federated trust with non-Microsoft IdPs, enabling organizations to adopt a best-of-breed identity strategy.
- Automated Identity Lifecycle Management: Uses Azure AD’s identity governance tools to provision, deprovision, and audit user access in real time, reducing manual errors by 60%.

Comparative Analysis
While FCS ADFS stands out in the identity federation space, it’s not the only solution. Below is a side-by-side comparison with leading alternatives:
| Feature | FCS ADFS | Azure AD Identity Protection | Okta Universal Directory | Ping Identity |
|---|---|---|---|---|
| Primary Use Case | Hybrid AD + cloud app SSO with protocol flexibility. | Cloud-native risk-based access and MFA. | SaaS-focused SSO with directory sync. | Enterprise-grade federation with customizable workflows. |
| Protocol Support | SAML 2.0, OAuth 2.0, OpenID Connect, WS-Fed. | OAuth 2.0, OpenID Connect (Azure AD-only). | SAML, OAuth 2.0, LDAP (limited). | SAML, OAuth 2.0, SCIM, RADIUS. |
| On-Premises Integration | Native AD/ADFS integration with hybrid cloud support. | Requires Azure AD Connect for on-prem sync. | Supports LDAP sync but lacks deep ADFS integration. | Full ADFS compatibility with custom connectors. |
| Conditional Access | Deep integration with Azure AD Conditional Access. | Built-in risk-based policies. | Limited to Okta-specific policies. | Customizable but requires PingOne add-ons. |
FCS ADFS excels in scenarios where organizations must maintain legacy AD dependencies while adopting cloud services. For purely cloud-native environments, Azure AD Identity Protection may suffice, but it lacks the protocol flexibility and on-premises depth of FCS ADFS. Okta and Ping Identity offer robust alternatives for SaaS-centric deployments, but their integration with ADFS is less seamless than Microsoft’s native solution.
Future Trends and Innovations
The next phase of FCS ADFS will likely focus on AI-driven identity governance, where machine learning models predict authentication risks in real time. Microsoft is already testing adaptive access policies that adjust dynamically based on user behavior—e.g., blocking logins from unusual geolocations or devices not previously associated with the account. This shift aligns with the zero-trust model, where never trust, always verify becomes the default posture.
Another emerging trend is the integration of decentralized identity protocols, such as DID (Decentralized Identifiers) and Verifiable Credentials. While still in experimental stages, these technologies could allow FCS ADFS to issue self-sovereign identity tokens, giving users greater control over their digital identities while reducing reliance on centralized IdPs. Early adopters in healthcare and finance are already piloting these models, with Microsoft positioning FCS ADFS as a potential bridge between traditional and decentralized identity systems.

Conclusion
FCS ADFS is more than a technical upgrade—it’s a strategic pivot toward identity architectures that are scalable, interoperable, and future-proof. The framework’s ability to harmonize legacy systems with cloud-native services makes it indispensable for enterprises navigating digital transformation. However, its success hinges on proper planning: organizations must assess their hybrid cloud maturity, define clear trust boundaries, and invest in training for administrators familiar with both ADFS and Azure AD.
The alternatives—whether Azure AD Identity Protection, Okta, or Ping Identity—each have their strengths, but none offer the same level of protocol agnosticism and hybrid flexibility as FCS ADFS. As identity threats grow more sophisticated, the ability to adapt authentication policies dynamically will become a competitive advantage. For enterprises committed to building resilient, user-centric identity ecosystems, FCS ADFS is not just a tool—it’s a foundation.
Comprehensive FAQs
Q: Can FCS ADFS replace traditional ADFS entirely?
A: While FCS ADFS can extend and modernize ADFS deployments, a full replacement isn’t recommended for organizations with heavy reliance on on-premises ADFS features like pass-through authentication or Web Application Proxy. Microsoft advises a phased migration, starting with cloud app federation before decommissioning legacy ADFS servers.
Q: How does FCS ADFS handle multi-factor authentication (MFA)?
A: FCS ADFS integrates with Azure MFA and third-party MFA providers via claims-based rules. For example, you can configure FCS ADFS to require MFA only for users accessing high-risk applications or from specific locations. The actual MFA challenge (e.g., SMS, authenticator app) is processed by Azure AD or the chosen IdP, while FCS ADFS manages the policy enforcement.
Q: What are the licensing costs for FCS ADFS?
A: FCS ADFS itself is free to use as it leverages existing Azure AD licenses (e.g., Azure AD Premium P1/P2). However, costs arise from:
- Azure AD licensing (required for cloud identity services).
- Windows Server licensing (if retaining on-premises ADFS for hybrid scenarios).
- Third-party IdP connectors (e.g., Okta, Ping Identity) if extending trust beyond Microsoft’s ecosystem.
Microsoft offers a Total Cost of Ownership (TCO) calculator to estimate hybrid identity deployments.
Q: Can FCS ADFS integrate with non-Microsoft identity providers?
A: Yes. FCS ADFS supports federated trust with any SAML 2.0 or OAuth 2.0-compliant IdP, including Okta, Ping Identity, and ForgeRock. The integration requires exchanging federation metadata (XML files) and configuring claim mappings. For example, an organization using Okta as its primary IdP can still federate AD users via FCS ADFS for legacy app access.
Q: What security risks should organizations watch for when deploying FCS ADFS?
A: The top risks include:
- Misconfigured Trust Relationships: Incorrectly defined federation metadata can lead to token spoofing or unauthorized access. Always validate metadata with tools like SAML Tracer.
- Certificate Expiry: FCS ADFS relies on digital certificates for token signing. Automate renewal processes to avoid service disruptions.
- Lateral Movement Risks: If FCS ADFS is compromised, attackers may pivot to on-premises AD. Mitigate this by enforcing least-privilege access and monitoring with Azure Sentinel.
- Protocol Misuse: OAuth 2.0 flows (e.g., implicit grant) can expose tokens to CSRF attacks. Restrict these flows to trusted applications only.
Microsoft’s Security Compliance Toolkit provides templates for hardening FCS ADFS deployments.
Q: How does FCS ADFS improve remote worker security?
A: FCS ADFS enhances remote security through:
- Conditional Access Policies: Blocks access from unmanaged devices or high-risk locations without requiring VPNs.
- Passwordless Authentication: Supports FIDO2 keys and biometric logins via Azure AD, reducing phishing risks.
- Session Management: Integrates with Azure AD’s Persistent Browser Session feature to maintain SSO across device reboots.
- Threat Intelligence Integration: Feeds risk signals from Azure Sentinel to dynamically adjust access rights.
For organizations with global teams, FCS ADFS can reduce VPN-related latency by up to 70% while maintaining security.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.