How to Enable JavaScript on Chrome: The Definitive Step-by-Step Manual

JavaScript isn’t just another feature—it’s the backbone of modern web experiences. Without it, dynamic content collapses into static shells, interactive forms freeze, and entire applications fail to load. Yet, despite its critical role, many users remain unaware of how to enable JavaScript on Chrome or why they might need to. The process is deceptively simple, but the consequences of misconfiguration—ranging from broken functionality to security vulnerabilities—are far from trivial.
The irony lies in Chrome’s default settings. While the browser ships with JavaScript enabled by default, corporate networks, restrictive IT policies, or outdated browser profiles often disable it silently. Developers and power users frequently encounter this issue when testing web applications, while casual users may stumble upon it when a website refuses to render properly. The solution isn’t just about flipping a switch; it’s about understanding the layers of control—from browser settings to system-wide policies—that govern JavaScript execution.
For those who’ve ever refreshed a page only to see a blank canvas where animations or forms should be, or for developers debugging client-side scripts, knowing how to enable JavaScript on Chrome isn’t just useful—it’s essential. Below, we dissect the mechanics, security trade-offs, and troubleshooting steps to ensure your browser behaves as intended.
The Complete Overview of How to Enable JavaScript on Chrome
JavaScript’s role in Chrome extends beyond mere functionality—it’s a cornerstone of performance optimization, security protocols, and user experience. When disabled, even the most basic tasks become cumbersome: think of a shopping cart that refuses to update, a real-time collaboration tool that fails to sync, or a single-page application that renders as a static PDF. The browser’s default behavior assumes JavaScript is safe to run, but this assumption breaks down in controlled environments like schools, enterprises, or public terminals where administrators enforce stricter security measures.The process of enabling JavaScript on Chrome is straightforward, but its effectiveness hinges on three variables: user permissions, system policies, and the browser’s internal state. A misconfigured group policy on a corporate machine, for instance, can override even the most explicit user settings. Similarly, extensions like ad blockers or privacy tools may interfere with script execution, requiring additional steps to bypass their restrictions. Understanding these variables is the first step toward resolving persistent issues.
Historical Background and Evolution
JavaScript’s origins trace back to 1995, when Netscape’s Brendan Eich created it in just 10 days to add interactivity to the web. Initially dismissed as a toy language, it evolved into a full-fledged programming language with frameworks like React, Angular, and Vue.js reshaping how applications are built. Chrome’s adoption of JavaScript wasn’t just about compatibility—it was about performance. Google’s V8 engine, introduced in 2008, revolutionized execution speed, making JavaScript a viable alternative to compiled languages for complex tasks.Over time, browsers adopted stricter security models to mitigate risks like cross-site scripting (XSS) attacks. Chrome’s Content Security Policy (CSP) and sandboxing mechanisms now restrict JavaScript execution by default in certain contexts, such as mixed-content warnings or third-party cookie blocks. This evolution reflects a broader trend: balancing functionality with security. For users, this means that enabling JavaScript on Chrome isn’t just about toggling a setting—it’s about navigating a landscape of layered protections designed to keep both users and developers safe.
Core Mechanisms: How It Works
At its core, JavaScript in Chrome operates within an isolated execution environment. When a script is loaded, the browser parses it, compiles it into bytecode via V8, and executes it in a sandboxed context. This isolation prevents malicious scripts from accessing sensitive data directly, but it also means that certain operations—like file system access or hardware control—require explicit permissions. The browser’s security model treats JavaScript as a privileged but contained resource, which is why disabling it can break features that rely on DOM manipulation or asynchronous operations.Table of Contents
- The Complete Overview of How to Enable JavaScript on Chrome
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Why does enabling JavaScript on Chrome keep getting reverted?
- Q: Can I enable JavaScript for specific sites only?
- Q: Does disabling JavaScript improve privacy?
- Q: Why does Chrome’s DevTools show JavaScript errors even after enabling it?
- Q: How do I enable JavaScript on Chrome for Android?
- Q: Is there a command-line method to enable JavaScript in Chrome?
- Q: What should I do if JavaScript is grayed out in settings?
- Q: Can JavaScript be enabled selectively for HTTPS sites only?
- Q: Why does enabling JavaScript slow down Chrome?
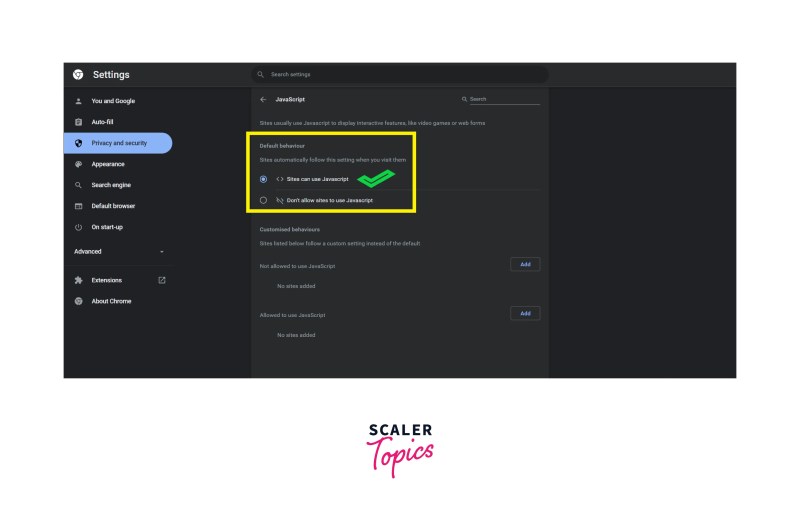
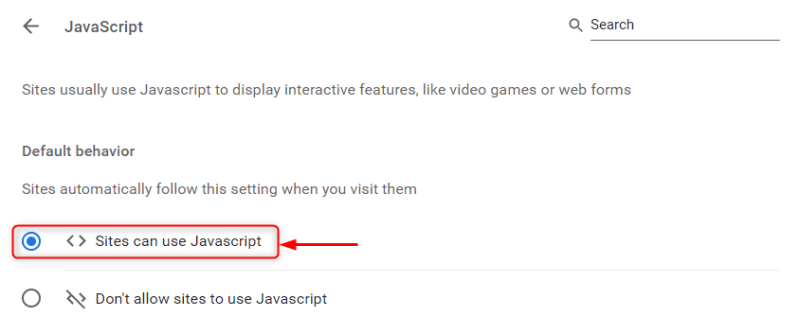
The actual toggle for enabling JavaScript on Chrome resides in the browser’s settings under Privacy and Security > Site Settings > JavaScript. However, this setting is merely the user-facing interface. Behind the scenes, Chrome’s policy engine evaluates system-level policies, extension rules, and even network-level restrictions (such as proxy configurations) before applying the change. For example, an enterprise policy might enforce `JavaScript=0` for all users, rendering the setting useless until the policy is modified by an administrator.
Key Benefits and Crucial Impact
JavaScript’s impact on Chrome isn’t just technical—it’s transformative. Without it, the web as we know it would revert to the early 2000s: static pages, clunky navigation, and minimal interactivity. Modern web apps, from Google Docs to interactive dashboards, rely on JavaScript to function. For developers, it’s the difference between debugging a static HTML file and troubleshooting a complex client-side application. Even for end users, the benefits are tangible: smoother animations, faster load times (via lazy loading), and seamless transitions between pages.The trade-off, however, is security. JavaScript’s power comes with risks—malicious scripts can hijack sessions, exfiltrate data, or exploit vulnerabilities in poorly coded applications. Chrome mitigates these risks through features like Content Security Policy headers, which restrict script sources, and the same-origin policy, which prevents cross-domain script interference. Yet, these safeguards don’t eliminate the need for caution. Users must weigh the convenience of enabled JavaScript against the potential for exploitation, especially on untrusted networks or sites.
"JavaScript is the Swiss Army knife of the web—versatile, powerful, and capable of cutting both ways." — Brendan Eich, Creator of JavaScript
Major Advantages
- Dynamic Content Rendering: JavaScript powers real-time updates, animations, and interactive elements (e.g., dropdown menus, sliders). Disabling it turns these into static placeholders.
- Performance Optimization: Frameworks like React and Angular use JavaScript to minimize server requests, reducing latency and improving load times.
- Cross-Platform Compatibility: Chrome’s V8 engine ensures JavaScript runs consistently across devices, from desktops to mobile browsers.
- Developer Tooling: Features like Chrome DevTools rely on JavaScript to inspect, debug, and profile web applications.
- Security Features: Modern JavaScript APIs (e.g., Web Crypto API) enable secure authentication and data encryption without plugins.
Comparative Analysis
| Feature | Chrome (JavaScript Enabled) | Chrome (JavaScript Disabled) |
|---|---|---|
| Interactive Elements | Fully functional (buttons, forms, animations) | Broken or non-responsive |
| Performance | Optimized for dynamic content | Degraded; relies on server-side rendering |
| Security Risk | Moderate (mitigated by sandboxing) | Lower (but misses modern protections) |
| Compatibility | Full support for modern web apps | Limited to static or server-rendered content |
Future Trends and Innovations
The future of JavaScript in Chrome is shaped by two competing forces: the demand for richer, more interactive web experiences and the need for tighter security. WebAssembly (WASM) is emerging as a complement to JavaScript, allowing near-native performance for computationally intensive tasks while maintaining security through sandboxing. Meanwhile, Chrome’s adoption of stricter privacy controls—such as blocking third-party cookies by default—will further restrict JavaScript’s capabilities unless developers adapt to first-party data models.Another trend is the rise of Progressive Web Apps (PWAs), which blend JavaScript-driven interactivity with offline capabilities. Chrome’s support for PWAs relies heavily on Service Workers, a JavaScript-based technology that enables background sync and push notifications. As PWAs become more prevalent, enabling JavaScript on Chrome won’t just be a technical requirement—it’ll be a necessity for accessing next-generation web applications.
Conclusion
Enabling JavaScript on Chrome is more than a checkbox exercise—it’s a gateway to the modern web. Whether you’re a developer testing an application, a user troubleshooting a broken site, or an administrator managing enterprise policies, understanding this process is critical. The key takeaway is balance: JavaScript unlocks functionality but demands vigilance. By leveraging Chrome’s built-in security features and staying informed about evolving best practices, users can harness its power without compromising safety.For those who’ve ever wondered why a website “just isn’t working,” the answer often lies in JavaScript. The solution, as outlined here, is within reach—provided you navigate the layers of settings, policies, and extensions that govern its execution.
Comprehensive FAQs
Q: Why does enabling JavaScript on Chrome keep getting reverted?
A: This typically happens due to group policies (on Windows) or managed configurations (in enterprise environments). If Chrome is part of a domain-joined network, an IT administrator may have enforced a policy to disable JavaScript. Check gpedit.msc (Windows) or contact your IT department for adjustments.
Q: Can I enable JavaScript for specific sites only?
A: Yes. In Chrome, navigate to Settings > Privacy and Security > Site Settings > JavaScript, then toggle "Allow" for individual sites. This is useful for balancing security and functionality on trusted domains.
Q: Does disabling JavaScript improve privacy?
A: Partially. While it blocks tracking scripts and ads, it also disables modern privacy features like Content Security Policy (CSP) and Web Crypto API. For better privacy, use extensions like uBlock Origin or Privacy Badger instead.
Q: Why does Chrome’s DevTools show JavaScript errors even after enabling it?
A: Errors may persist due to:
- Corrupted browser cache (clear via
Ctrl+Shift+Del) - Conflicting extensions (disable ad blockers temporarily)
- Mixed content warnings (HTTP/HTTPS mismatches)
Q: How do I enable JavaScript on Chrome for Android?
A: Open Chrome > tap the three-dot menu > Settings > Site Settings > JavaScript. Toggle it on. Note: Some Android devices with work profiles (e.g., corporate phones) may override this setting.
Q: Is there a command-line method to enable JavaScript in Chrome?
A: Yes. Launch Chrome with the flag --disable-javascript removed from shortcut properties or use the policy flag --js-flags="--disable" (requires admin rights). For enterprise deployments, modify the policies.json file to include "JavaScript": "Enabled".
Q: What should I do if JavaScript is grayed out in settings?
A: A grayed-out option indicates restricted permissions. Try:
- Running Chrome as an administrator (Windows)
- Disabling conflicting extensions
- Resetting Chrome settings via
chrome://settings/reset
Q: Can JavaScript be enabled selectively for HTTPS sites only?
A: Chrome doesn’t offer a built-in toggle for HTTPS-only JavaScript, but you can use extensions like "ScriptSafe" to enforce stricter rules. Alternatively, configure a custom Content Security Policy (CSP) via the site’s HTTP headers to restrict scripts to secure contexts.
Q: Why does enabling JavaScript slow down Chrome?
A: JavaScript-heavy sites (e.g., those using React or heavy animations) increase CPU usage. To mitigate this:
- Use Chrome’s Task Manager (
Shift+Esc) to kill resource-hogging tabs. - Disable unnecessary extensions.
- Enable Hardware Acceleration in Chrome settings.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.