The America Remote Access Complete Guide: Mastering Secure Work from Anywhere
Remote access in America isn’t just a convenience—it’s a strategic imperative for businesses navigating hybrid workforces, global teams, and cybersecurity threats. The shift from office-bound operations to seamless connectivity has redefined productivity, but without the right infrastructure, even the most advanced companies risk exposure, latency, or compliance violations. Whether you’re a multinational corporation managing distributed teams or a freelancer relying on secure connections, understanding the America remote access complete guide framework is non-negotiable.
The stakes are higher than ever. A single misconfigured VPN or unpatched remote desktop protocol can leave sensitive data vulnerable to state-sponsored actors or ransomware gangs—both of which have escalated attacks on U.S. infrastructure by 400% since 2020. Meanwhile, regulations like the California Consumer Privacy Act (CCPA) and HIPAA impose strict requirements on data handling, forcing organizations to balance accessibility with airtight security. The tools you deploy today must anticipate tomorrow’s threats, from quantum-resistant encryption to zero-trust architectures.
This guide cuts through the noise to deliver actionable insights on selecting, implementing, and optimizing remote access solutions tailored to the American market. From enterprise-grade zero-trust networks to consumer-friendly cloud-based tools, we dissect the mechanics, weigh the trade-offs, and forecast where the industry is headed—without the fluff.
The Complete Overview of America Remote Access Solutions
America’s remote access landscape is a patchwork of technologies, each serving distinct needs across industries. At its core, remote access enables users to interact with internal systems, applications, or data as if they were physically present—whether from a coffee shop in Chicago or a co-working space in San Francisco. The solutions range from Virtual Private Networks (VPNs) for basic encryption to Remote Desktop Protocol (RDP) for granular control, and cloud-based access brokers that integrate with identity providers like Okta or Azure AD. What unites them is a shared challenge: reconciling speed, security, and scalability in an era where remote work is no longer optional.The complexity lies in the trade-offs. A VPN, for example, offers simplicity but struggles with performance over long distances, while Software-Defined Wide Area Networking (SD-WAN) optimizes bandwidth at the cost of higher implementation costs. Meanwhile, Just-In-Time (JIT) access solutions like BeyondTrust or CyberArk mitigate credential theft but require rigorous identity verification—adding friction for legitimate users. The America remote access complete guide must account for these variables, starting with an understanding of how the ecosystem evolved.
Historical Background and Evolution
The foundations of remote access were laid in the 1980s with dial-up modems, a clunky but revolutionary way for employees to check emails or update databases from home. By the 1990s, the rise of ISDN lines and early VPNs (using Point-to-Point Tunneling Protocol, or PPTP) allowed for encrypted connections, though performance remained a bottleneck. The real inflection point came in the 2000s with broadband internet, which enabled IPsec VPNs—still the gold standard for many enterprises today—to deliver stable, encrypted tunnels. However, these solutions were rigid, requiring static IP addresses and manual configuration, which proved cumbersome for growing teams.The turning point arrived with cloud computing and Software as a Service (SaaS) in the late 2010s. Platforms like Citrix Virtual Apps and Microsoft Remote Desktop Services (RDS) shifted access from on-premises servers to scalable, web-based interfaces. Simultaneously, the zero-trust model emerged as a response to high-profile breaches (e.g., SolarWinds, 2020), advocating for never trust, always verify principles. Today, the America remote access complete guide reflects this evolution: a hybrid approach where legacy systems coexist with cutting-edge AI-driven threat detection and multi-factor authentication (MFA).
Core Mechanisms: How It Works
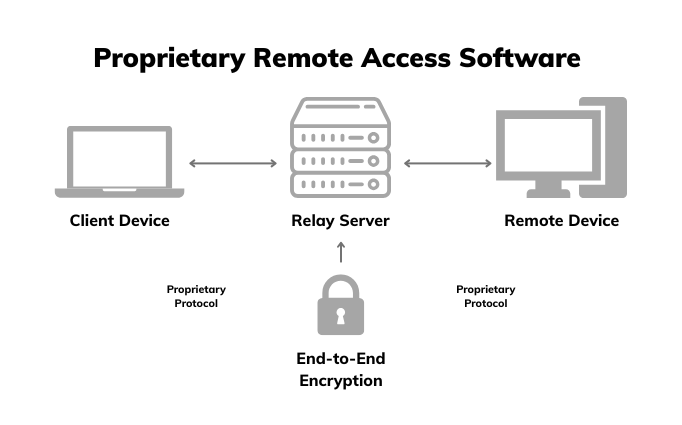
Under the hood, remote access relies on three pillars: authentication, encryption, and session management. Authentication begins with credentials (passwords, biometrics, or hardware tokens) verified against a directory service like Active Directory or LDAP. Once validated, the user’s device establishes an encrypted tunnel—typically via TLS (Transport Layer Security) or IPSec—to prevent eavesdropping. The tunnel routes traffic through a gateway (e.g., a VPN server or cloud access broker), which may enforce additional policies like device compliance checks or geofencing to block access from high-risk regions.Table of Contents
- The Complete Overview of America Remote Access Solutions
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: What’s the most secure remote access method for a small business in America?
- Q: How can I reduce latency for remote access in the U.S.?
- Q: Are there free remote access tools that meet compliance standards?
- Q: How do I ensure my remote access setup complies with U.S. state laws?
- Q: What’s the difference between RDP and VDI, and which should I choose?
- Q: Can I use a consumer VPN for business remote access?
Session management dictates how the connection behaves. Persistent connections (common in RDP) maintain an active session until manually terminated, while ephemeral sessions (used in zero-trust models) expire after a set time or upon inactivity. Performance hinges on latency optimization techniques such as TCP acceleration or WebRTC, which reduce lag for real-time applications like video conferencing. The America remote access complete guide emphasizes that no single mechanism fits all use cases—enterprises must align their stack with workflow demands, whether prioritizing low-latency access for traders or high-security access for healthcare records.
Key Benefits and Crucial Impact
The adoption of remote access solutions in America has reshaped industries, from finance (where latency-sensitive trading relies on low-millisecond VPNs) to healthcare (where HIPAA-compliant RDP secures patient data). For businesses, the benefits are quantifiable: Gartner estimates that organizations with mature remote access strategies see 30% higher employee productivity and 40% lower operational costs by reducing office space requirements. Yet, the impact extends beyond metrics—it’s a cultural shift. Teams now collaborate across time zones, reducing the need for overtime and fostering diversity by enabling global talent pools.The flip side is risk. A 2023 Ponemon Institute report found that 63% of U.S. companies experienced a remote access-related breach in the past year, with credential theft and misconfigured VPNs as top attack vectors. The stakes are clear: without a robust America remote access complete guide-aligned strategy, the cost of downtime or regulatory fines can dwarf the savings from remote work. Balancing innovation with security requires a disciplined approach—one that starts with understanding the core advantages of modern solutions.
"Remote access isn’t just about connectivity—it’s about trust. The organizations that thrive will be those who treat every connection as a potential entry point for adversaries." — John Kindervag, Co-founder of Zero Trust Exchange
Major Advantages
- Global Workforce Enablement: Break geographical barriers by granting secure access to employees in Mexico, Canada, or offshore hubs without compromising data sovereignty. Solutions like Cloudflare Access or Zscaler Private Access ensure compliance with FERPA, GDPR, and state-specific laws.
- Cost Efficiency: Reduce overhead by eliminating the need for branch offices and cutting expenses on hardware maintenance (e.g., thin clients vs. full desktop deployments). Cloud-based RDP services like Amazon WorkSpaces offer pay-as-you-go pricing models.
- Disaster Recovery and Business Continuity: Multi-region failover ensures uptime during outages. Tools like Citrix DaaS replicate virtual desktops across AWS and Azure, minimizing downtime during cyberattacks or natural disasters.
- Enhanced Security Posture: Zero-trust architectures (e.g., BeyondTrust’s Privileged Access Management) limit lateral movement by adversaries, while AI-driven anomaly detection (e.g., CrowdStrike Falcon) flags suspicious behavior in real time.
- Scalability for Startups and Enterprises: Containerized remote access (e.g., Docker + VPN) allows startups to spin up secure environments on demand, while enterprises leverage SD-WAN for dynamic bandwidth allocation during peak usage.

Comparative Analysis
| Solution Type | Best For |
|---|---|
| Traditional VPN (e.g., OpenVPN, Fortinet) | Legacy systems, cost-sensitive SMBs, or teams requiring site-to-site encryption. Struggles with modern web apps (e.g., SaaS) and high-latency use cases. |
| Zero-Trust Network Access (ZTNA, e.g., Cloudflare Access) | Regulated industries (healthcare, finance) where least-privilege access is critical. Ideal for cloud-first enterprises but requires identity provider integration. |
| Remote Desktop Services (RDS, e.g., Microsoft RDS) | Knowledge workers needing full desktop environments (e.g., CAD designers, developers). High licensing costs and scalability limits for large teams. |
| Cloud-Based Access Brokers (e.g., Okta Universal Directory) | Hybrid environments with mixed on-prem/cloud apps. Simplifies SSO and MFA but may introduce vendor lock-in risks. |
Future Trends and Innovations
The next frontier in America remote access solutions is AI-driven automation. Tools like Palo Alto’s Prisma Access already use machine learning to optimize routing, but upcoming advancements will include predictive threat blocking—where AI preemptively isolates devices showing early signs of compromise. Quantum-resistant encryption (e.g., NIST’s CRYSTALS-Kyber) is another priority, as quantum computers threaten to break current RSA and ECC algorithms by 2030.Beyond technology, regulatory shifts will dictate adoption. The SEC’s cybersecurity disclosure rules (2023) now require public companies to report breaches within four days, incentivizing real-time monitoring in remote access stacks. Meanwhile, state-level privacy laws (e.g., Virginia’s CDPA) will push organizations to adopt data residency controls, complicating cross-border access. The America remote access complete guide must prepare for these changes by adopting modular, compliance-ready architectures that can pivot as laws evolve.

Conclusion
The America remote access complete guide isn’t a static document—it’s a living framework that evolves with threats, regulations, and user demands. The organizations that succeed will be those who treat remote access as a strategic asset, not an afterthought. This means auditing legacy systems, training employees on phishing-resistant MFA, and investing in observability tools to detect anomalies before they escalate.For individuals, the takeaway is simpler: security is personal. Whether you’re a remote worker using Tailscale or a CISO deploying Pulse Secure, the principles remain the same—verify, encrypt, and monitor. The future of remote access in America won’t belong to the fastest or the cheapest, but to those who balance speed, security, and scalability with precision.
Comprehensive FAQs
Q: What’s the most secure remote access method for a small business in America?
A: For SMBs, a zero-trust solution like Cloudflare Access or Tailscale’s WireGuard-based VPN offers the best balance of security and ease of use. Avoid open-source VPNs without hardening (e.g., unconfigured OpenVPN) and prioritize MFA + device posture checks. If handling PHI or PCI data, pair with a HIPAA-compliant HSM like AWS CloudHSM.
Q: How can I reduce latency for remote access in the U.S.?
A: Latency depends on distance, ISP quality, and protocol. Use SD-WAN (e.g., VMware SD-WAN) to dynamically route traffic over the fastest path, or deploy edge computing (e.g., Fastly) to cache frequently accessed apps. For real-time applications, WebRTC-based solutions (e.g., Jitsi Meet) outperform traditional VPNs. Test with ping tests (e.g., `ping google.com`) and traceroute to identify bottlenecks.
Q: Are there free remote access tools that meet compliance standards?
A: Most free tools (e.g., TeamViewer Free, AnyDesk) lack enterprise-grade encryption or audit logs, making them unsuitable for HIPAA, GDPR, or SOX compliance. For free but compliant options, consider:
- ProtonVPN (open-source, no-logs policy)
- WireGuard (self-hosted, audit-proof)
- Nextcloud Talk (self-hosted video conferencing with end-to-end encryption)
Q: How do I ensure my remote access setup complies with U.S. state laws?
A: Compliance varies by state. For California (CCPA), ensure:
- Data minimization (only collect necessary user data)
- Right to opt-out (via Usercentrics CookieConsent)
- Data residency controls (store data in AWS GovCloud or Google Cloud’s U.S. regions)
Q: What’s the difference between RDP and VDI, and which should I choose?
A: RDP (Remote Desktop Protocol) is a Microsoft protocol that streams a full desktop session from a host machine (e.g., Windows Server). VDI (Virtual Desktop Infrastructure) is an architecture where virtual machines (e.g., VMware Horizon) host desktops, accessed via RDP or HTML5 clients.
- Choose RDP if you need low-cost, simple access to a single machine (e.g., for IT admins managing servers).
- Choose VDI for scalable, multi-user environments (e.g., call centers, engineering teams) with centralized management.
Q: Can I use a consumer VPN for business remote access?
A: No. Consumer VPNs (e.g., NordVPN, ExpressVPN) lack:
- Enterprise-grade logging/auditing (critical for SOX, HIPAA)
- Split tunneling controls (exposes local traffic to risks)
- Dedicated bandwidth (shared servers cause jitter/lag)
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.