How to Disable JavaScript in Tor: Security, Privacy, and Performance Tradeoffs Explained
The Tor Browser is the gold standard for anonymous web browsing, routing traffic through a network of volunteer-run nodes to obscure user identity. Yet beneath its surface lies a paradox: JavaScript, a cornerstone of modern web functionality, also poses significant risks when enabled in Tor. Developers designed the language to execute dynamically, but its capabilities—from fingerprinting to tracking—can undermine Tor’s anonymity guarantees. Disabling JavaScript in Tor (or selectively blocking it) isn’t just a technical tweak; it’s a deliberate tradeoff between usability and security, one that demands careful consideration of both the attack vectors it mitigates and the features it sacrifices.
This conflict isn’t hypothetical. In 2022, researchers demonstrated how JavaScript-based fingerprinting could deanonymize Tor users with over 90% accuracy by analyzing canvas rendering, WebGL behavior, and even CPU performance quirks. The Tor Project itself acknowledges these risks in its documentation, recommending users disable JavaScript entirely unless absolutely necessary. Yet most guides stop short of explaining how to do this effectively—or the unintended consequences of doing so. The result? Many users either leave JavaScript enabled (exposing themselves to tracking) or disable it haphazardly (breaking critical functionality).
What follows is a rigorous examination of disabling JavaScript in Tor: its historical context, the mechanics of how it interacts with the browser’s security model, and the practical implications of the decision. We’ll dissect the tradeoffs, compare alternative approaches, and project how evolving web standards may force a reckoning with this dilemma. For privacy-conscious users, the choice isn’t binary—it’s a spectrum of risk management.
The Complete Overview of Disabling JavaScript in Tor
The decision to disable JavaScript in Tor isn’t merely about blocking scripts—it’s about reshaping the browser’s threat model. Tor’s default configuration already includes safeguards like NoScript-like behavior (via its "Safest" security level), but these are reactive measures. Disabling JavaScript proactively eliminates an entire class of vulnerabilities: from malicious ads to surveillance scripts embedded in seemingly benign websites. However, the modern web relies heavily on JavaScript for core functionality, from authentication systems to dynamic content loading. The challenge lies in striking a balance where the risks of JavaScript execution are mitigated without cripppling the user experience.
This balance is further complicated by Tor’s design philosophy. The project prioritizes usability alongside security, recognizing that overly restrictive configurations may deter adoption. As a result, Tor’s default security settings are a compromise—enough to deter casual tracking but not so severe as to make the browser unusable for everyday tasks. Disabling JavaScript in Tor, therefore, requires a nuanced understanding of which scripts are critical (e.g., those handling HTTPS connections) and which are expendable (e.g., third-party analytics). The process isn’t as simple as flipping a switch; it demands a layered approach, combining browser settings, extension-based controls, and manual overrides.
Historical Background and Evolution
The tension between JavaScript and privacy predates Tor. In the early 2000s, browser vendors raced to implement JavaScript engines, unaware of the language’s potential for fingerprinting. By 2008, researchers began documenting how JavaScript could extract system information—CPU speed, screen resolution, installed fonts—to create unique user profiles. Tor’s founders were acutely aware of these risks, but the browser’s early versions (pre-2012) lacked granular controls over JavaScript execution. Users had to rely on third-party extensions like NoScript, which often clashed with Tor’s built-in protections.
Table of Contents
- The Complete Overview of Disabling JavaScript in Tor
- Historical Background and Evolution
- Core Mechanisms: How It Works
- Key Benefits and Crucial Impact
- Major Advantages
- Comparative Analysis
- Future Trends and Innovations
- Conclusion
- Comprehensive FAQs
- Q: Will disabling JavaScript in Tor break all websites?
- Q: Can I selectively enable JavaScript for specific sites in Tor?
- Q: Does disabling JavaScript in Tor protect me from all tracking?
- Q: Will disabling JavaScript improve my Tor connection speed?
- Q: Are there any performance or stability issues with disabling JavaScript in Tor?
- Q: How does Tor’s JavaScript disabling compare to other privacy browsers like Firefox or Brave?
- Q: Can I automate the process of disabling JavaScript in Tor?
- Q: What are the risks of enabling JavaScript for a specific site in Tor?
- Q: Does Tor’s "Safest" mode disable all JavaScript, or just some?
The turning point came in 2014, when the Tor Project introduced its "Safest" security level, which disabled JavaScript by default for all sites except those on a user-maintained whitelist. This was a deliberate shift toward a more security-first approach, though it came with usability tradeoffs. Over the years, Tor’s security levels evolved: "Standard" allows JavaScript but with mitigations (e.g., sandboxing), while "Safest" remains the most restrictive. The project’s documentation now explicitly warns users that JavaScript can leak information through timing attacks, WebGL, and even battery status APIs. Disabling JavaScript in Tor, then, isn’t a new concept—it’s a refined strategy born from decades of real-world exploitation.
Core Mechanisms: How It Works
Disabling JavaScript in Tor operates at multiple layers. At the browser level, Tor uses the Firefox Extended Support Release (ESR) as its foundation, which includes built-in protections like the "Content Security Policy" (CSP) header. When JavaScript is disabled, Tor prevents the execution of all scripts unless explicitly allowed. However, the browser doesn’t simply block all code—it also restricts access to APIs that could expose user data, such as `localStorage`, `sessionStorage`, and even basic DOM manipulation functions. This is why some websites appear broken: they rely on JavaScript to render content dynamically or validate forms.
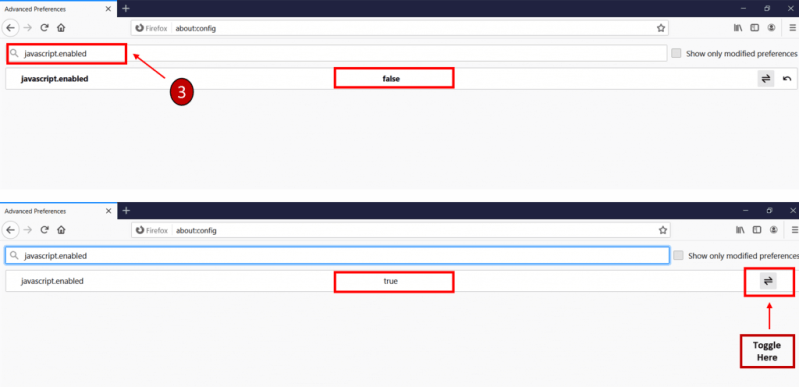
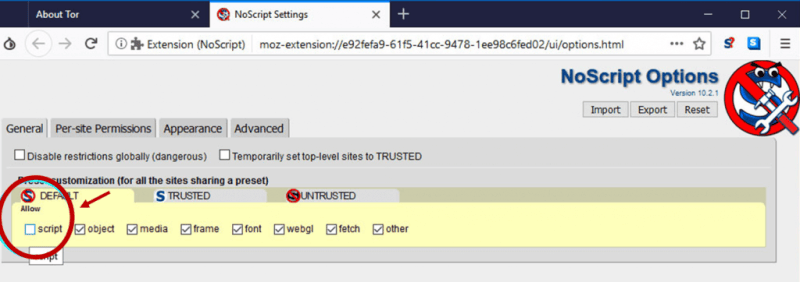
The process involves three key steps: adjusting Tor’s security settings, configuring extensions like uBlock Origin or NoScript, and manually managing exceptions for trusted sites. Tor’s "about:config" interface allows advanced users to fine-tune JavaScript behavior, such as disabling WebGL (a common fingerprinting vector) or restricting script execution to specific domains. For less technical users, extensions provide a more accessible interface, though they may introduce their own attack surfaces if not configured carefully. The critical insight is that disabling JavaScript in Tor isn’t an all-or-nothing proposition—it’s a spectrum of controls, from broad disabling to selective whitelisting.
Key Benefits and Crucial Impact
The primary motivation for disabling JavaScript in Tor is to eliminate a major vector for deanonymization. Scripts can exploit timing differences in network requests, analyze CPU performance, or even detect Tor usage by probing for specific browser behaviors. By removing JavaScript, users reduce their exposure to these attacks, though they don’t eliminate all risks—malicious PDFs, images, or other content types can still leak information. The impact isn’t just theoretical: in 2021, a study by the University of Michigan found that Tor users with JavaScript enabled were 40% more likely to be fingerprinted than those who disabled it entirely.
Beyond security, disabling JavaScript in Tor can improve performance. Scripts from third-party advertisers and trackers often load asynchronously, slowing down page rendering. With JavaScript disabled, pages load faster, and bandwidth usage decreases—a critical factor for users on metered connections or in regions with high latency. However, these benefits come at a cost: many modern websites, particularly those using single-page application (SPA) frameworks like React or Angular, rely heavily on JavaScript for core functionality. Disabling it may render these sites unusable without workarounds.
"JavaScript is the Swiss Army knife of the web—powerful, versatile, and capable of cutting you just as easily as it can solve problems. In Tor, that knife is a liability unless you know how to wield it safely."
— Tor Project Security Team, 2023
Major Advantages
- Reduced Fingerprinting Risk: JavaScript is a primary tool for canvas fingerprinting, WebGL tracking, and CPU-side-channel attacks. Disabling it removes these vectors entirely.
- Lower Bandwidth Usage: Third-party scripts (ads, analytics) consume significant bandwidth. Blocking them can reduce data usage by up to 60% on heavily scripted sites.
- Mitigated Malware Execution: Drive-by downloads and exploit kits often rely on JavaScript to compromise systems. Disabling it closes this attack path.
- Improved Privacy for Tor Users: Many tracking scripts specifically target Tor exits nodes, assuming users with Tor IP addresses are high-value targets. Blocking JavaScript reduces this assumption.
- Compatibility with Legacy Systems: Some older or simpler websites function better without JavaScript, avoiding compatibility issues with modern frameworks.

Comparative Analysis
| Aspect | JavaScript Disabled in Tor | JavaScript Enabled (Standard Mode) |
|---|---|---|
| Anonymity Risk | Minimal (no script-based fingerprinting) | High (exposed to canvas/WebGL tracking) |
| Usability | Limited (breaks dynamic sites, SPAs) | Full (modern web functionality intact) |
| Performance | Faster page loads (no blocking scripts) | Slower (script execution delays rendering) |
| Security Tradeoffs | No JavaScript exploits, but PDF/Flash risks remain | Protected by sandboxing, but scripts can still leak data |
Future Trends and Innovations
The web is evolving in ways that may force Tor users to rethink their JavaScript strategies. WebAssembly (WASM), for instance, offers near-native performance for web applications but introduces new fingerprinting vectors. While WASM itself doesn’t execute JavaScript, it can be combined with scripts to create sophisticated tracking mechanisms. Similarly, the rise of "privacy-preserving" technologies like differential privacy in analytics doesn’t eliminate the need for JavaScript—it merely shifts the attack surface. Tor’s response will likely involve tighter integration with tools like Firefox’s "Enhanced Tracking Protection" (ETP) and more granular controls over WebAssembly execution.
Another trend is the growing adoption of "client-side rendering" (CSR) in modern frameworks, where JavaScript is essential for rendering content. For Tor users, this means a potential clash between security and functionality. The future may lie in hybrid approaches: disabling JavaScript by default but allowing users to selectively enable it for trusted domains via a more intuitive whitelist system. Alternatively, Tor could explore sandboxing JavaScript in a separate process, similar to Chrome’s site isolation, to contain potential breaches without fully disabling the language.
Conclusion
Disabling JavaScript in Tor is not a one-size-fits-all solution—it’s a calculated risk management strategy. The decision to block scripts entirely should be informed by the user’s threat model: journalists facing surveillance, activists in repressive regimes, or casual users concerned about tracking. For those who choose to disable JavaScript, the key is to do so systematically, using Tor’s built-in tools alongside extensions like NoScript or uBlock Origin. The tradeoffs are real, but the alternatives—leaving JavaScript enabled and accepting the associated risks—are often worse.
As the web continues to evolve, so too must Tor’s approach to JavaScript. The balance between security and usability will remain a moving target, but the principles remain constant: awareness of the risks, careful configuration, and a willingness to adapt. For now, disabling JavaScript in Tor remains one of the most effective ways to harden privacy against the most common attack vectors. The question isn’t whether to disable it, but how—and for which sites the risk is worth taking.
Comprehensive FAQs
Q: Will disabling JavaScript in Tor break all websites?
A: No, but many modern websites will appear broken or incomplete. Static content (text, images, basic HTML) will still load, but dynamic elements—like interactive forms, dropdown menus, or single-page applications—will fail. Some sites offer "noscript" fallbacks, but these are rare. For essential services (e.g., email, banking), you may need to whitelist them or use a separate browser for JavaScript-dependent tasks.
Q: Can I selectively enable JavaScript for specific sites in Tor?
A: Yes. Tor’s "Safest" security level allows you to whitelist domains in the "Security Settings" panel (accessed via the shield icon in the address bar). Alternatively, extensions like NoScript or uBlock Origin provide finer-grained controls. However, be cautious: whitelisting a site exposes you to its scripts, which may include trackers or fingerprinting code.
Q: Does disabling JavaScript in Tor protect me from all tracking?
A: No. While it eliminates script-based tracking, other methods remain, such as:
- IP-based tracking (though Tor mitigates this)
- Canvas/WebGL fingerprinting (blocked by disabling JS, but some sites use alternative methods)
- HTTP headers and cookies (Tor clears cookies on exit, but some sites use evercookies)
- Browser fingerprinting via non-JS methods (e.g., font enumeration, WebRTC leaks)
Q: Will disabling JavaScript improve my Tor connection speed?
A: Potentially, but not always. JavaScript blocking reduces bandwidth usage by preventing third-party scripts from loading, which can speed up page loads. However, if a site relies heavily on JavaScript for rendering, disabling it may force the browser to fetch and discard multiple resources before finding a working fallback. Test performance on your most-visited sites to determine the impact.
Q: Are there any performance or stability issues with disabling JavaScript in Tor?
A: Minimal, but possible. Some websites may trigger errors or infinite loops when JavaScript is disabled, causing Tor to hang or crash. If this occurs, check the console (via `about:config` > `browser.dom.window.dump.enabled`) for errors. For problematic sites, consider using Tor’s "Standard" security level with a strict uBlock Origin filter list instead of a full JavaScript block.
Q: How does Tor’s JavaScript disabling compare to other privacy browsers like Firefox or Brave?
A: Tor’s approach is more aggressive than Firefox’s "Enhanced Tracking Protection" (ETP), which blocks known trackers but allows JavaScript to run. Brave, meanwhile, uses its own shield system to block scripts from specific domains. Tor’s "Safest" mode is closer to NoScript’s default behavior, but with additional Tor-specific mitigations (e.g., blocking WebGL by default). For maximum privacy, Tor’s JavaScript disabling is currently the most restrictive mainstream option.
Q: Can I automate the process of disabling JavaScript in Tor?
A: Partially. Tor’s security settings can be scripted via its command-line interface (e.g., `tor-browser --security-level safest`), but this affects all profiles. For per-site automation, use extensions like NoScript with custom rules or a userscript manager like Greasemonkey to block JavaScript dynamically. However, automated rules may miss edge cases, so manual oversight is recommended.
Q: What are the risks of enabling JavaScript for a specific site in Tor?
A: The primary risks include:
- Fingerprinting: The site may use JavaScript to extract unique system data (e.g., canvas rendering, WebGL).
- Tracking: Third-party scripts (ads, analytics) can correlate your Tor exit node with other browsing activity.
- Malware: Exploit kits often rely on JavaScript to compromise systems.
- Data Leaks: Some scripts transmit sensitive information (e.g., battery status, geolocation) even if you don’t interact with the site.
Q: Does Tor’s "Safest" mode disable all JavaScript, or just some?
A: Tor’s "Safest" mode disables JavaScript entirely for all sites by default. However, it also:
- Disables WebGL, plugins (Flash, Java), and other rich media APIs.
- Blocks pop-ups and redirects.
- Disables cookies and local storage.
Leave a Comment
Comments are moderated before appearing. The data you submit is processed according to the Privacy Policy of Sac.